
What is CNAPP (Cloud-Native Application Protection Platform)?
A CNAPP is a unified cloud native application protection platform that safeguards multi-cloud ecosystems. Find out how it improves cloud and cybersecurity.
Key Takeaways
- What it is: A single platform that consolidates cloud security from code commit through production runtime, replacing fragmented point tools.
- What it unifies: CSPM, KSPM, CWPP, CIEM, IaC scanning, and CDR — correlated into prioritized, exploitable attack paths across multi-cloud and hybrid environments.
- Why runtime matters: Live workload telemetry detects active threats and attack paths that posture and vulnerability data alone cannot catch.
- How it helps teams: Fewer alerts, earlier developer feedback in CI/CD, faster remediation, and built-in compliance evidence.
- Where it's heading: AI-powered risk scoring, agentless and agent-based hybrid coverage, and autonomous remediation.
- SentinelOne: Singularity™ Cloud Security delivers CNAPP in a single agent and agentless platform with AI-powered runtime protection and automated remediation.
What is CNAPP?
A CNAPP is a unified cloud security platform that protects cloud-native applications and infrastructure across the application lifecycle, from development and infrastructure as code (IaC) through deployment and production runtime.
CNAPP consolidates multiple cloud security capabilities, including Cloud Security Posture Management (CSPM), Cloud Workload Protection (CWPP), Cloud Infrastructure Entitlement Management (CIEM), Kubernetes Security Posture Management (KSPM), vulnerability management, IaC security, and cloud detection and response (CDR), into an integrated approach.
Instead of managing separate security tools for cloud configuration, identities, workloads, vulnerabilities, and runtime threats, a CNAPP correlates these security signals to provide greater visibility into cloud risk, prioritize the risks that matter most, and help security and development teams remediate issues earlier.
In simple terms, CNAPP helps organizations secure cloud-native applications from code to cloud and runtime.
Why is CNAPP Important?
Traditional security tools and approaches are limited to protecting only on-premises data centers and endpoints. They don’t protect cloud native apps and services by design. As we’re migrating towards cloud native technologies and changing, ephemeral ecosystems, there is a need for stronger security automation, faster releases, and the implementation of modern DevSecOps practices.
As organizations scale their cloud environments, security teams must be able to:
- Discover cloud assets and understand their relationships
- Identify vulnerable code, images, and infrastructure configurations
- Control excessive permissions and standing privileges
- Detect malicious activity in production
- Correlate isolated findings into meaningful attack paths
- Prioritize remediation according to business impact and exploitability
- Maintain evidence for regulatory and internal compliance
- Apply controls without unnecessarily slowing development
Gartner Recommendations for CNAPP
Gartner recommends security teams and risk management leaders who are responsible for cloud security strategies to research, analyze, and evaluate emerging CNAPP offerings. A Cloud Native Application Protection Platform addresses the full life cycle protection requirements of cloud-native apps and infrastructure from development to production. Attack surfaces are expanding and modern CNAPP solutions will focus on securing runtime environments, especially networks, compute, storage, identities and permissions, and other cloud security controls.
It predicts that 60% of organizations that don’t deploy a unified CNAPP solution within their cloud infrastructure will lack extensive visibility into their cloud attack surfaces. Without CNAPP, companies will fail to meet their zero-trust security goals and this will be a reality in 2029. Surges in cloud threats have also spiked rapid adoption of CNAPPs for cloud-native security.
Gartner’s Magic Quadrant reveals key capabilities of CNAPP technologies and provides deeper insights into various IT and cloud security products and services, including their customized use cases.

CNAPP Market Guide
Get key insights on the state of the CNAPP market in this Gartner Market Guide for Cloud-Native Application Protection Platforms.
Core Components of CNAPP
A Cloud-Native Application Protection Platform comes with various key components that enable the protection of each stage of the software development life cycle, right up to production environments. The table below breaks down each component and what it does.
Component | What It Does |
CSPM (Cloud Security Posture Management) | Finds misconfigurations and compliance gaps across cloud accounts and services. |
CWPP (Cloud Workload Protection) | Protects running workloads, containers, and serverless functions from runtime threats. |
CIEM (Cloud Infrastructure Entitlement Management) | Maps identity permissions across cloud resources and flags excessive access. |
KSPM (Kubernetes Security Posture Management) | Secures Kubernetes clusters, configurations, and access controls. |
Vulnerability Management | Identifies and prioritizes known vulnerabilities across cloud workloads and images. |
IaC Security | Scans infrastructure-as-code templates for misconfigurations before deployment. |
CDR (Cloud Detection and Response) | Detects and responds to active threats using runtime and control-plane signals. |
How Does CNAPP Secure AI Workloads and Pipelines?
A CNAPP secures AI workloads by applying its existing posture, identity, workload, and data-security components to models, training data, and inference pipelines, treating a misconfigured AI service like any other exposed cloud asset.
AI-specific risks a CNAPP addresses:
- Exposed or misconfigured AI model endpoints and inference APIs
- Overprivileged service accounts and roles used by AI pipelines
- Sensitive or regulated data in training sets without adequate access controls
- Unmonitored third-party AI services and shadow AI usage
- Vulnerable dependencies in AI and ML frameworks and container images
CSPM checks the configuration of managed AI services, CIEM governs which identities can reach models and training data, CWPP protects the compute running inference and training, and DSPM tracks exposure of the data feeding those pipelines. That gives one correlated risk view instead of a separate AI security tool bolted onto the rest of the stack.
Securing the infrastructure around a model is different from securing the model's inputs and outputs. Prompt injection, jailbreaks, and unsafe generative AI usage fall to SentinelOne's Prompt Security, not CNAPP; see the SentinelOne section below for where AI Security Posture Management(AI SPM) fits into this same picture.
How CNAPP Works?
A CNAPP works by pulling telemetry from every stage of the cloud-native lifecycle into one place, correlating it, and acting on what it finds.
Collecting telemetry from across the environment
A CNAPP pulls data continuously from cloud provider APIs, container registries, Kubernetes clusters, code repositories, and identity providers, along with any third-party security tools already in place. Agentless scanning covers an entire cloud account within minutes with no footprint on the workload, while a dedicated agent adds real-time runtime visibility and forensics down to the process level for workloads that need it.
Correlating signals into one view
That telemetry flows into a shared data lake or console instead of sitting in separate scan reports. From there, a CNAPP correlates processes, events, and activity in real time to identify actual exploit paths, chains where a misconfiguration, a vulnerability, and an identity connect into something an attacker could use, rather than treating each finding as an isolated issue. Dashboards give security teams one at-a-glance view of the entire cloud estate instead of five separate tool outputs to reconcile by hand.
Enforcing policy and automated response
A unified console makes it possible to apply consistent policy across multi-cloud and hybrid environments instead of managing rules separately per platform. When a CNAPP identifies an active threat, it can quarantine the affected workload, rotate exposed secrets, or trigger other response actions without waiting on a human to act first, freeing security teams to focus on investigation instead of routine cleanup.
CNAPP vs CSPM
Here are a few critical differences between CNAPP vs CSPM:
- CSPM cannot issue security alerts to users or give insights into cloud workloads. It can’t prioritize security risks or give full environmental context. CSPM solutions cannot detect lateral movements within networks. CNAPP can do all of this.
- CNAPP solutions give comprehensive reporting capabilities, analytics, and intelligent threat remediation. They provide complete agentless security coverage and can centralize cloud security insights.
- CNAPP includes CSPM, KSPM, CWPP, CDR, and a host of other security tools and features. It also streamlines governance, compliance, and reduces the risk of misconfigurations by security cloud-native apps. CNAPP can also manage user account permissions and enhance cloud security posture as a whole.
Explore the differences in detail: CNAPP vs. CSPM
Challenges in Implementing CNAPP
Implementing a CNAPP is a substantial step toward unified cloud security, but it’s rarely plug-and-play. Preparation and awareness of common pitfalls will help you navigate these hurdles more smoothly.
- Skill Gaps & Culture Shifts: One of the biggest challenges is building the proper skill set across Development, Security, and Operations teams. Confusion abounds if your DevOps engineers aren’t familiar with how CNAPP integrates into CI/CD pipelines or if your security analysts don’t grasp containerization intricacies. A mismatch in expertise can lead to neglected features or underused automation. Overcoming this starts with targeted training, cross-functional workshops, and possibly collaborating with a trusted vendor or consultant.
- Organizational Complexity: Companies usually have siloed departments, with developers, operations, and security working in separate vacuums. Combining all these teams under one CNAPP can create role overlap and workflow conflicts. To address such complexities, break down barriers by mapping each team’s responsibilities. Foster cross-team communication and align everyone around shared goals for improved security posture and operational efficiency.
- High Integration Effort: Even though CNAPP solutions integrate multiple capabilities, they must mesh with your unique environment. They must adapt to and work with cloud service providers, code repositories, and existing security or SIEM tools. You should expect a phased rollout that might require custom connectors, API calls, or plugin development. Underestimating this integration can balloon deployment timelines and sabotage user acceptance.
- Alert Fatigue & Data Overload: When large-scale data ingestion isn’t correctly tuned, you risk generating a flood of alerts and noise. The teams get accustomed to the flood, and it misses or delays detecting real threats. It mostly leads to unanswered vulnerabilities or compliance gaps. Overcome this by putting robust prioritization and correlation workflows in place. Work on labeling your alerts based on severity, potential exploitability, and the level of impact on critical assets.
- Change Management will affect your overall security posture, budgeting, and procurement processes. With clear change management plans, you avoid internal resistance, overshadowed success metrics, or slow adoption. Develop a roadmap that defines short-term wins and long-term milestones to ensure your organization stays motivated and aligns around the new processes CNAPP introduces.
Benefits of Using CNAPP
- Unified cloud visibility: Correlates security issues, events, and logs across your entire multi-cloud footprint in a single view. Surfaces hidden attack vectors through visualizations and real-time alerts.
- Risk-based prioritization: Delivers remediation guidance so teams act on the risks that matter most. Deeper visibility into misconfigurations and compliance gaps supports faster, better-informed decisions.
- Faster threat detection and response: Embeds security checks at every phase of the DevOps cycle, catching risks before they reach production. Enables a proactive stance that stops incidents before they escalate into breaches.
- Reduced tool complexity: Replaces standalone CSPM, runtime protection, and alert-correlation tools with one platform. Cuts licensing costs, administrative overhead, and integration work.
- Better collaboration between security and development teams: Distributes security ownership through built-in guardrails instead of centralizing it with one team. Reduces friction between security and DevOps, so developers can secure their own code without slowing down releases.
CNAPP Best Practices
CNAPP can offer complete visibility and control over your cloud infrastructure. Also, CNAPP can secure public, private, hybrid, single, and even multi-clouds. CNAPP solutions give you access to metrics and KPIs needed to continuously monitor your environments without restricting workflows or disrupting business operations.
Here are of the best CNAPP practices to follow for security professionals:
Adopt shift-left security from day one: Scan infrastructure-as-code templates, container images, and code repositories before they reach production. Catching misconfigurations early, for example, through automated checks on every pull request, prevents costly rework and security gaps down the line.
- Automate policy enforcement: Define rules for resource configurations, identity permissions, and container security that your CNAPP enforces automatically, such as keeping S3 buckets private by default or blocking privileged Kubernetes pods. This reduces manual triage and frees your team to focus on strategy.
- Prioritize alerts by risk: Configure your CNAPP to categorize vulnerabilities into severity tiers and map each tier to a clear response workflow. This ensures critical threats get immediate attention while lower-priority issues are tracked for later remediation.
- Apply zero-trust and least-privilege access: Use cloud infrastructure entitlement management (CIEM) and role-based access control to limit users and workloads to only the access they need. This reduces lateral movement risk and limits the blast radius of any breach.
- Build in continuous feedback: Treat your CNAPP as a living system rather than a static tool. Refine detection logic based on real-world findings, for example, adjusting severity classifications when the platform's output doesn't match actual impact, so the platform becomes more accurate over time.
CNAPP Use Cases in Cloud Security
Here are some of the most popular CNAPP use cases in cloud security:
Containerized environments & DevSecOps: Scans container images in the registry, validates configurations against best practices, and monitors pods at runtime, catching insecure builds before they go live.
- AI & machine learning deployments: Flags misconfigurations and vulnerabilities across ML frameworks, GPU instances, and data stores, with consistent policy enforcement across the AI pipeline.
- Retail & eCommerce in multi-cloud: Unifies security across AWS, Azure, and on-prem environments under a single console, with automated posture checks and alerting for fast fixes during high-traffic periods.
- Healthcare & financial services compliance: Maps resources against HIPAA, PCI DSS, and GDPR in real time, with automated evidence collection that simplifies audits and reduces breach risk.
- Remote & hybrid workforce protection: Locks down overly permissive roles, flags suspicious sign-ins, and secures ephemeral infrastructure regardless of where users connect from.
How to Choose the Right CNAPP for Your Organization?
You should pick a CNAPP that aligns with your business goals. It will involve balancing technical, operational, and budget considerations. Here’s what you need to look for:
- Scope & Coverage: Confirm that the platform supports your cloud environments and workloads (VMs, containers, serverless).
- Integration Ease: Look for compatibility with your CI/CD pipelines, code repositories, and security infrastructure. More straightforward integrations reduce adoption friction.
- AI & Automation Features: Evaluate how advanced the platform’s analytics are—effective machine learning can drastically reduce false positives and speed response times.
- Customizability: Assess whether you can easily define custom detection rules, compliance checks, and workflows to match specific security or regulatory needs.
- Vendor Support & Expertise: The best CNAPP providers offer robust documentation, training, and specialized expertise to help your organization during implementation.
CNAPP Buyer’s Guide
Learn everything you need to know about finding the right Cloud-Native Application Protection Platform for your organization.
Level Up Your Cloud Security with SentinelOne’s Comprehensive CNAPP
SentinelOne’s Singularity™ Cloud Security is a unified Cloud Native Application Protection Platform for enterprises. It is the world’s most advanced autonomous cybersecurity solution. It is also an AI-enhanced CNAPP that grants access to integrated and world-class threat intelligence.
Singularity™ Cloud Security offers no-code hyper automation, can prioritize fixes with Verified Exploit Paths™, and comes with an AI security analyst.
Here’s what it can do:
- Agentless Rapid Deployment: Spin up posture management in minutes—no need to install software on each workload. Automated scans immediately inventory your cloud environments for vulnerabilities, misconfigurations, and compliance risks.
- Deep Protection using a Runtime agent: For critical workloads, a runtime agent provides real-time detection of ransomware, zero-day exploits, and fileless attacks. You can gain forensic telemetry and near-instant rollback capabilities if threats materialize.
- Cloud Security Posture Management (CSPM): Full compliance checks, hyper-automation for policy enforcement, and a graph-based asset inventory let you quickly find and fix critical misconfigurations.
- Vulnerability Management & Shift-Left Container Scanning: SentinelOne covers the entire development lifecycle; it can scan code repositories, CI/CD pipelines, and secure container registries to prevent vulnerabilities from reaching production.
- AI Security Posture Management: Discover AI pipelines, analyze AI data model configurations, and uncover verified exploit paths for AI services.
- External Attack Surface Management: Automate pen testing and exploit path discovery to ensure that hidden assets or incorrectly exposed services don’t become high-risk blind spots.
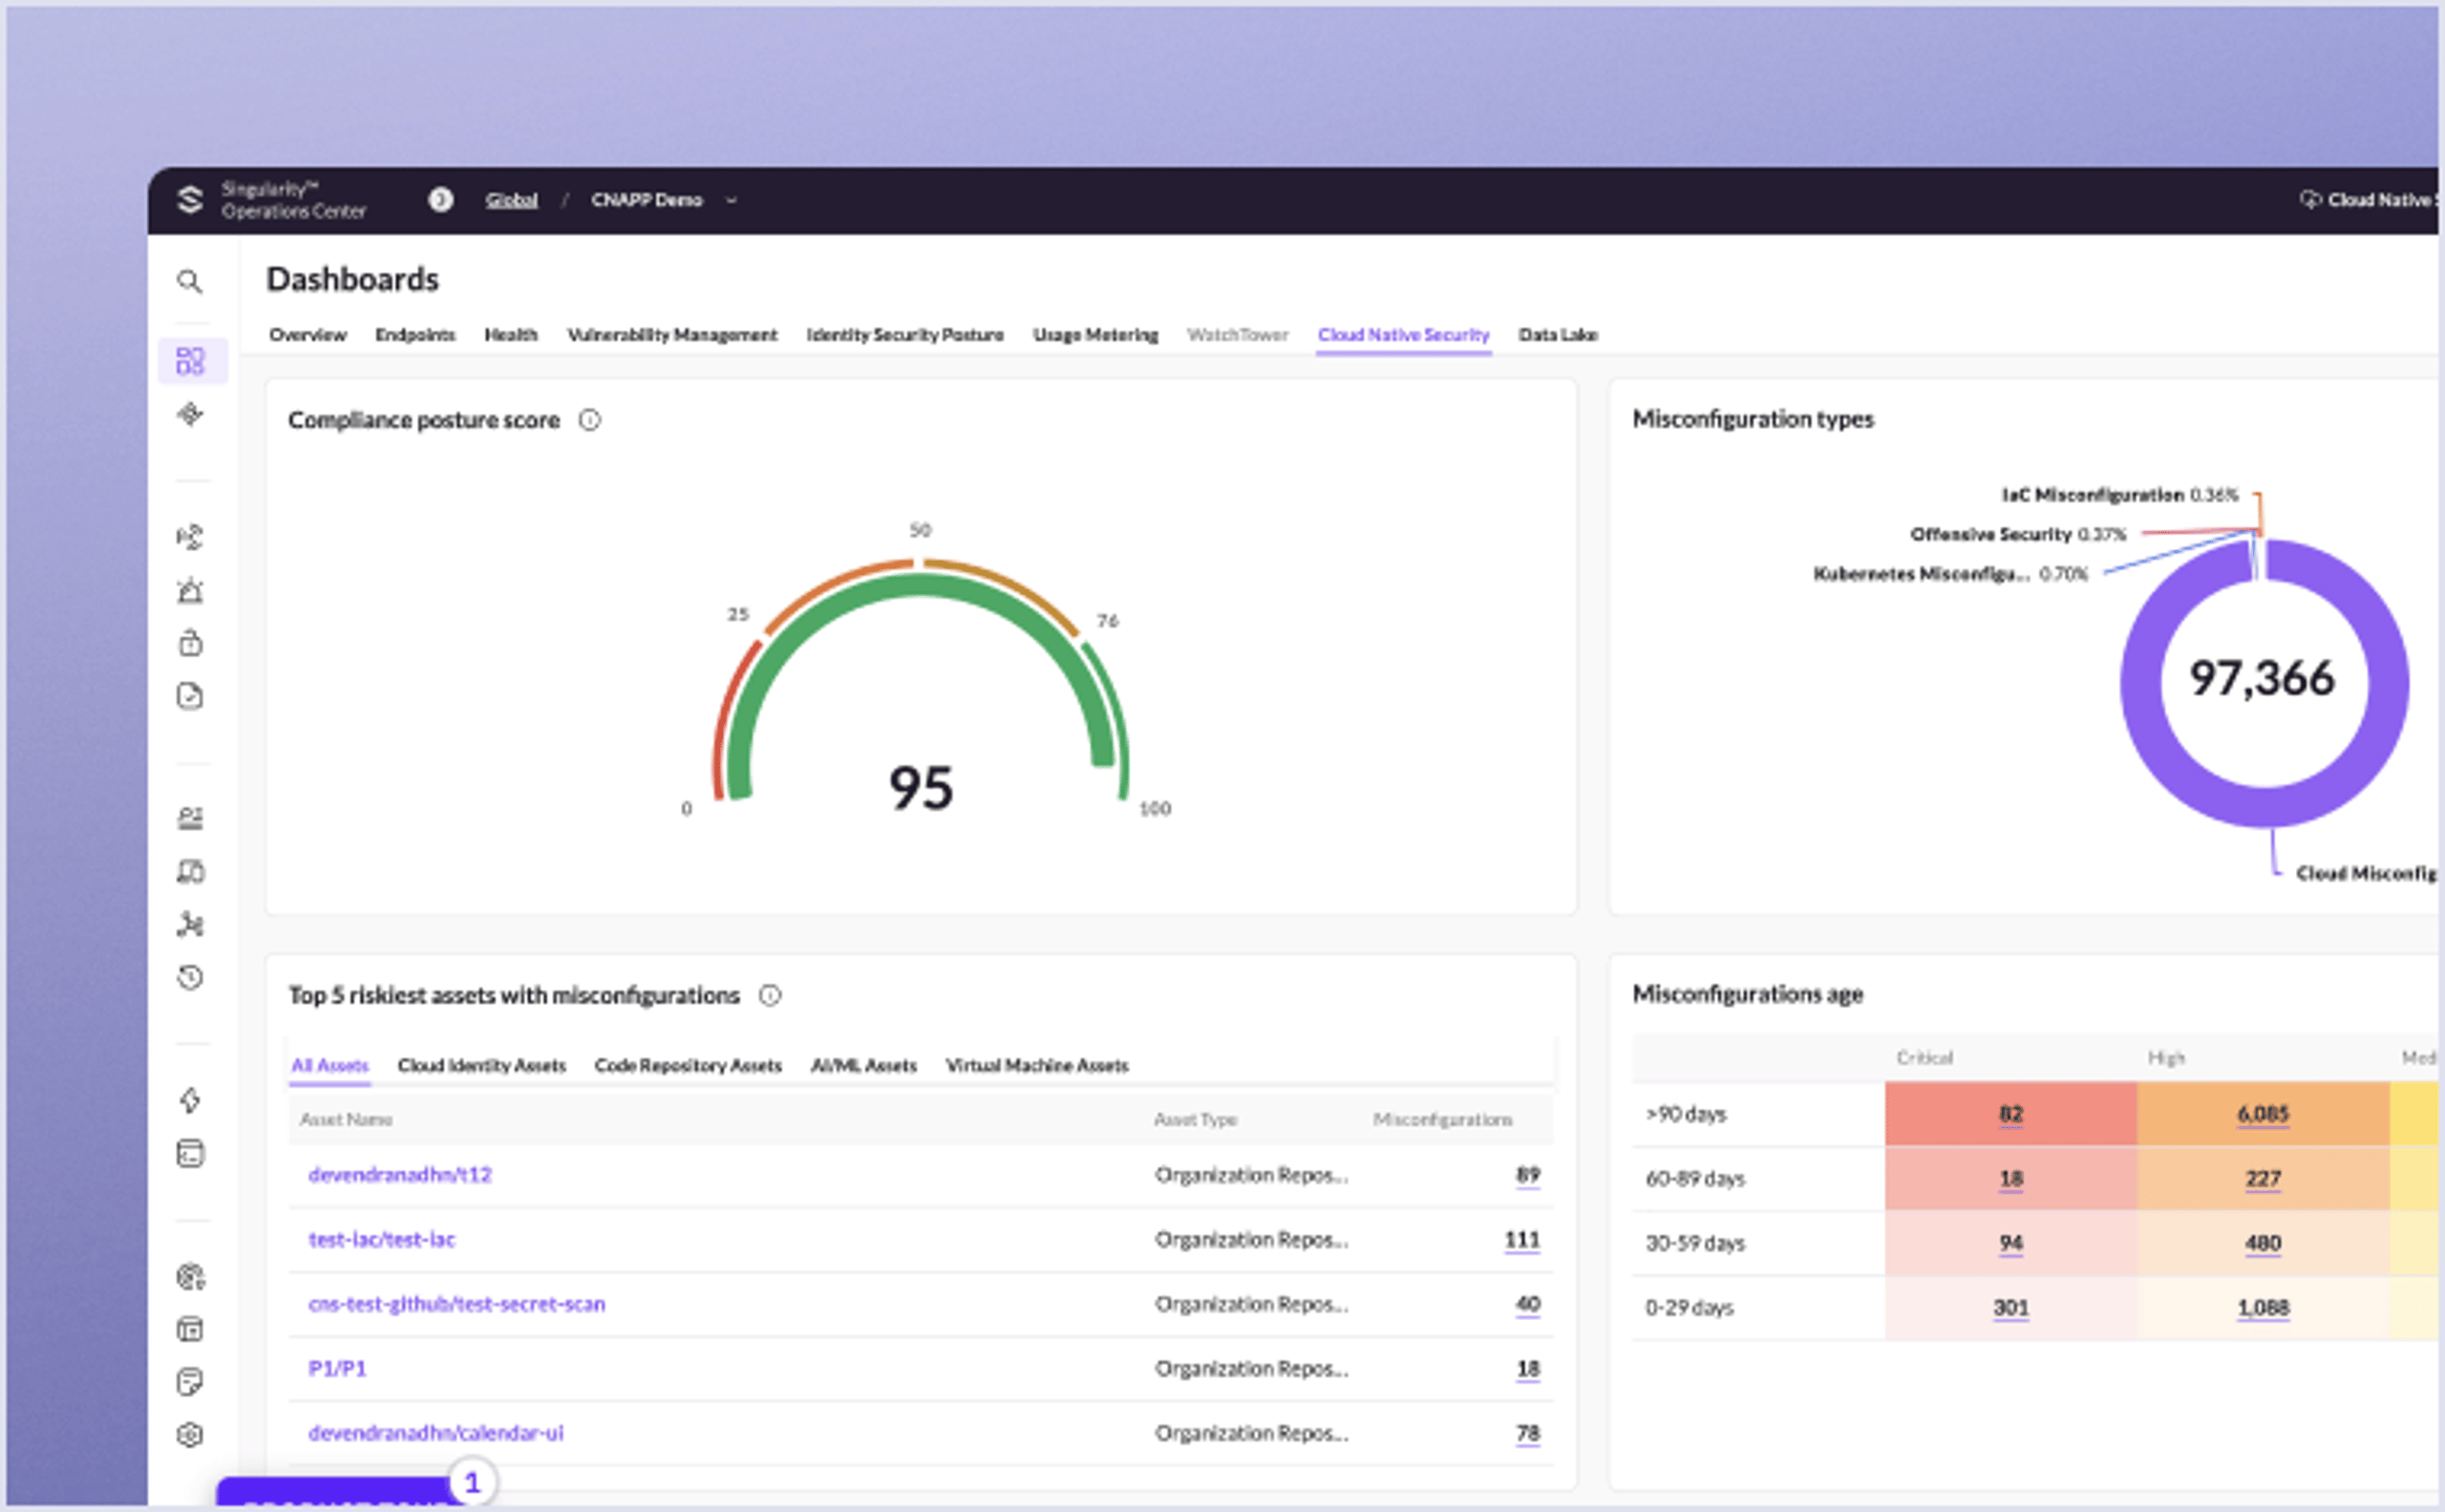
Combine evidence-backed risk reduction with autonomous response with the most evolved, AI-powered CNAPP.
Conclusion
You have seen how Cloud-Native Application Protection Platforms can integrate your cloud assets under one security framework, filling gaps that traditional tools cannot fill. Adopting a CNAPP approach is securing containers and virtual machines and establishing a forward-thinking defense strategy that meets the demands of rapid development and evolving threats.
CNAPP provides integrated policy enforcement, automated detection and response, and a culture of continuous improvement to transform complex cloud ecosystems into resilient, secure environments, from fragmented solutions to an all-in-one platform that protects your applications throughout their cloud journey. Try SentinelOne today.
See SentinelOne in Action
Discover how AI-powered cloud security can protect your organization in a one-on-one demo with a SentinelOne product expert.
CNAPP FAQs
A CNAPP is an integrated security solution that protects cloud-native applications during development and production. It encapsulates various tools, including CSPM, CWPP, and CIEM, in one place.
CNAPP is a complete cloud security platform that protects your cloud-native workloads and infrastructure throughout their entire lifecycle. It tackles cloud misconfigurations, vulnerability scanning, runtime threats, and data security for applications running in cloud environments. CASB sits between users and cloud services to enforce security policies and protect your data. They watch access to SaaS applications, monitor user behavior and help prevent data breaches. CNAPP secures cloud infrastructure from the inside, while CASB guards the gates to cloud services.
CNAPP protects your cloud workloads and applications where they live, focusing on infrastructure security, container protection, and runtime threats. It monitors cloud configurations and secures development pipelines for cloud-native applications. SASE is a networking framework that combines SD-WAN with security services to secure user access to applications from anywhere. It includes ZTNA, secure web gateways, and firewall services delivered from the cloud edge. CNAPP secures the applications themselves, while SASE secures how users connect to those applications. They work together for complete cloud protection.
Yes. You can make multi-cloud compliance easy with CNAPP solutions. It makes PCI DSS, HIPAA, and SOC 2 regulations easier to comply with.
CNAPP provides end-to-end visibility and constant compliance checks, which is helpful for highly regulated industries such as finance, healthcare, and government.
Look for capabilities such as CSPM integrated, runtime protection, AI-driven threat detection, IaC scanning, and robust identity governance.
Yes. CNAPP platforms unify security policies and streamline visibility across AWS, Azure, GCP, and private clouds.
A CNAPP that scales can be right-sized for SMBs, with automated security not requiring large in-house teams.
Advanced CNAPP solutions use machine learning and runtime analysis to detect anomalous behavior, such as zero days and other emerging threats.
CNAPP locks down container images, detects misconfigurations in Kubernetes or Docker, and delivers real-time runtime protection.
Pricing varies depending on the scale of infrastructure, features, and vendor. However, less need for individual standalone tools often saves much money in the long run.
Discover More About Cloud Security



Your Cloud Security—Fully Assessed in 30 Minutes.
Meet with a SentinelOne expert to evaluate your cloud security posture across multi-cloud environments, uncover cloud assets, misconfigurations, secret scanning, and prioritize risks with Verified Exploit Paths™.
