Prevention
Zero Trust, Applied to Execution.
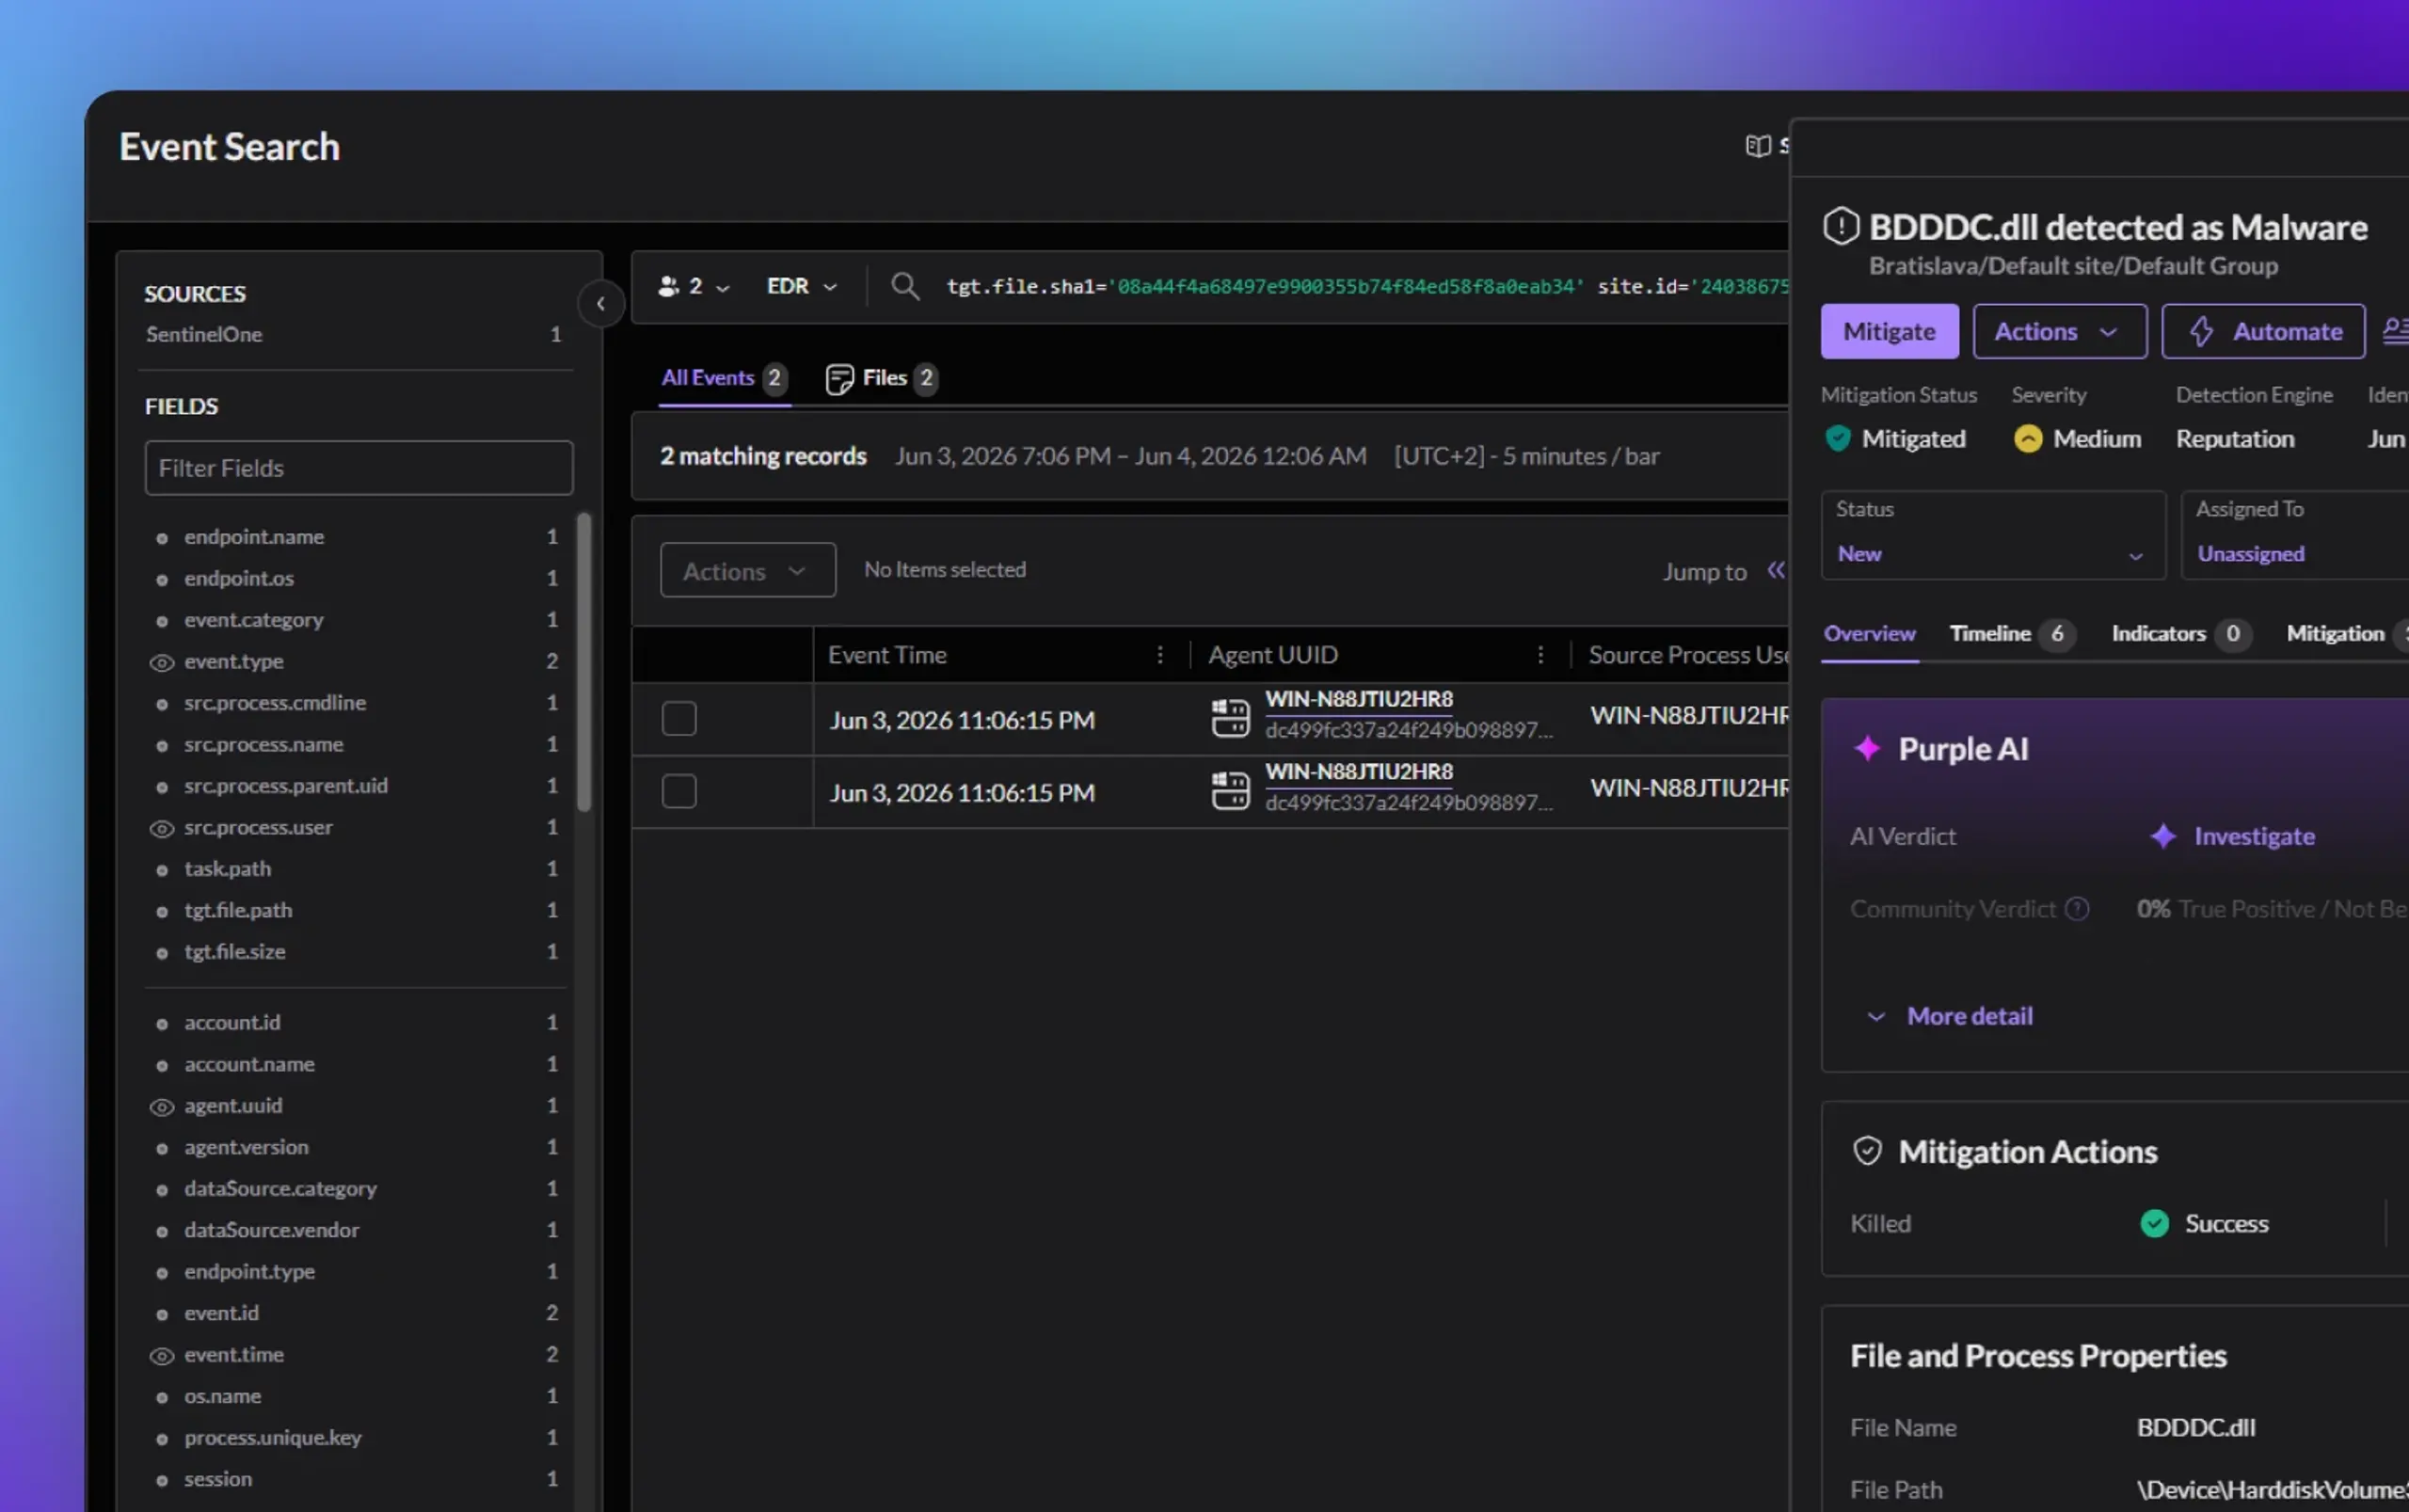
Nothing is trusted to run by default. Policy-based allowlisting blocks unauthorized applications before they execute. Blocklisting adds a second layer against known bad software.
Block execution by publisher, path, hash, or process
Combine allowlisting and blocklisting in a single policy
Catch living-off-the-land techniques like launching PowerShell from Word