Singularity™ Complete

Reduce complexity, improve your security posture, and seamlessly integrate powerful AI to protect endpoints, servers, and cloud workloads.

Glowing translucent purple nested rectangular frames forming a diagonal tunnel shape on a black background
  • Block Attacks with Machine Speed

    Improve visibility, proactively prevent malware, and reduce your attack surface to minimize the risk of compromise.

  • Detect & Investigate with AI

    Leverage behavioral AI to detect ransomware and zero days, and augment threat hunting and investigation with an AI security analyst.

  • Respond Autonomously

    Automate incident response with policy or use remediation actions including patented 1-click rollback.

  • Manage at Scale

    Optimize operations with automated deployment of a resource-efficient, unified agent, and get 24/7 support with an always-on interactive AI support agent.

AI-Powered Endpoint & Cloud Security

Secure your organization with enterprise-wide protection, detection, and response capabilities, supercharged by advanced AI.
01
Abstract atom-like orbital graphic on a black background with a glowing gradient sphere and purple node circles on intersecting elliptical paths

Protect Endpoints & Cloud Workloads

  • Improve visibility with a unified agent that provides the industry’s best operating system and cloud environment coverage, plus advanced telemetry collection.

  • Block malware with autonomous, machine-speed prevention, powered by on-device AI.

  • Reduce your attack surface with continuous visibility and minimize the risk of compromise.

  • Take a unified inventory with unmanaged endpoint and cloud discovery.
02
Abstract dark geometric design with outlined hexagons in pink and green dots, connected by beams to a stacked rounded rectangle frame

Detect, Investigate, and Hunt with Speed and Accuracy

  • Detect ransomware and zero days with superior behavioral and static AI models that accurately identify suspicious and malicious patterns in real time on servers, workstations, and workloads.

  • Conduct faster threat hunting and investigations at scale with Purple AI natural language queries (with multi-language support).

  • Save time with Purple AI-generated event summaries and self-documenting notebooks.

  • Automatically correlate telemetry data from endpoints, cloud workloads, and identity sources to create a detailed, visual story of the event.

03
Neon green and magenta hexagon network with connected nodes and diagonal line on a dark abstract black background

Rapidly Respond and Remediate

  • Automate incident response with policy or use remediation actions, including patented 1-click rollback.

  • Reduce mean time to respond (MTTR) with automated responses and prevention mechanisms, all in one code base.

  • Quickly block incoming and outgoing network activity, eliminating the risk of an infection spreading across your network.

  • Investigate attacks, collect forensic data, and remediate breaches faster with Full Remote Shell.

04
Black abstract geometric design with translucent gray rectangular frames, magenta line path, and green-to-blue gradient strip

Scale and Manage with Ease

  • Optimize operations with a single, resource-efficient agent that incorporates endpoint, identity, and cloud, and delivers streamlined capabilities and administration through a shared agent and interface.

  • Achieve faster resolution with 24/7 support, including an always-on interactive AI support agent.

  • Enable your system to operate out of kernel space (including eBPF).

  • Get up and running fast with automated deployment and DevOps tools.

05
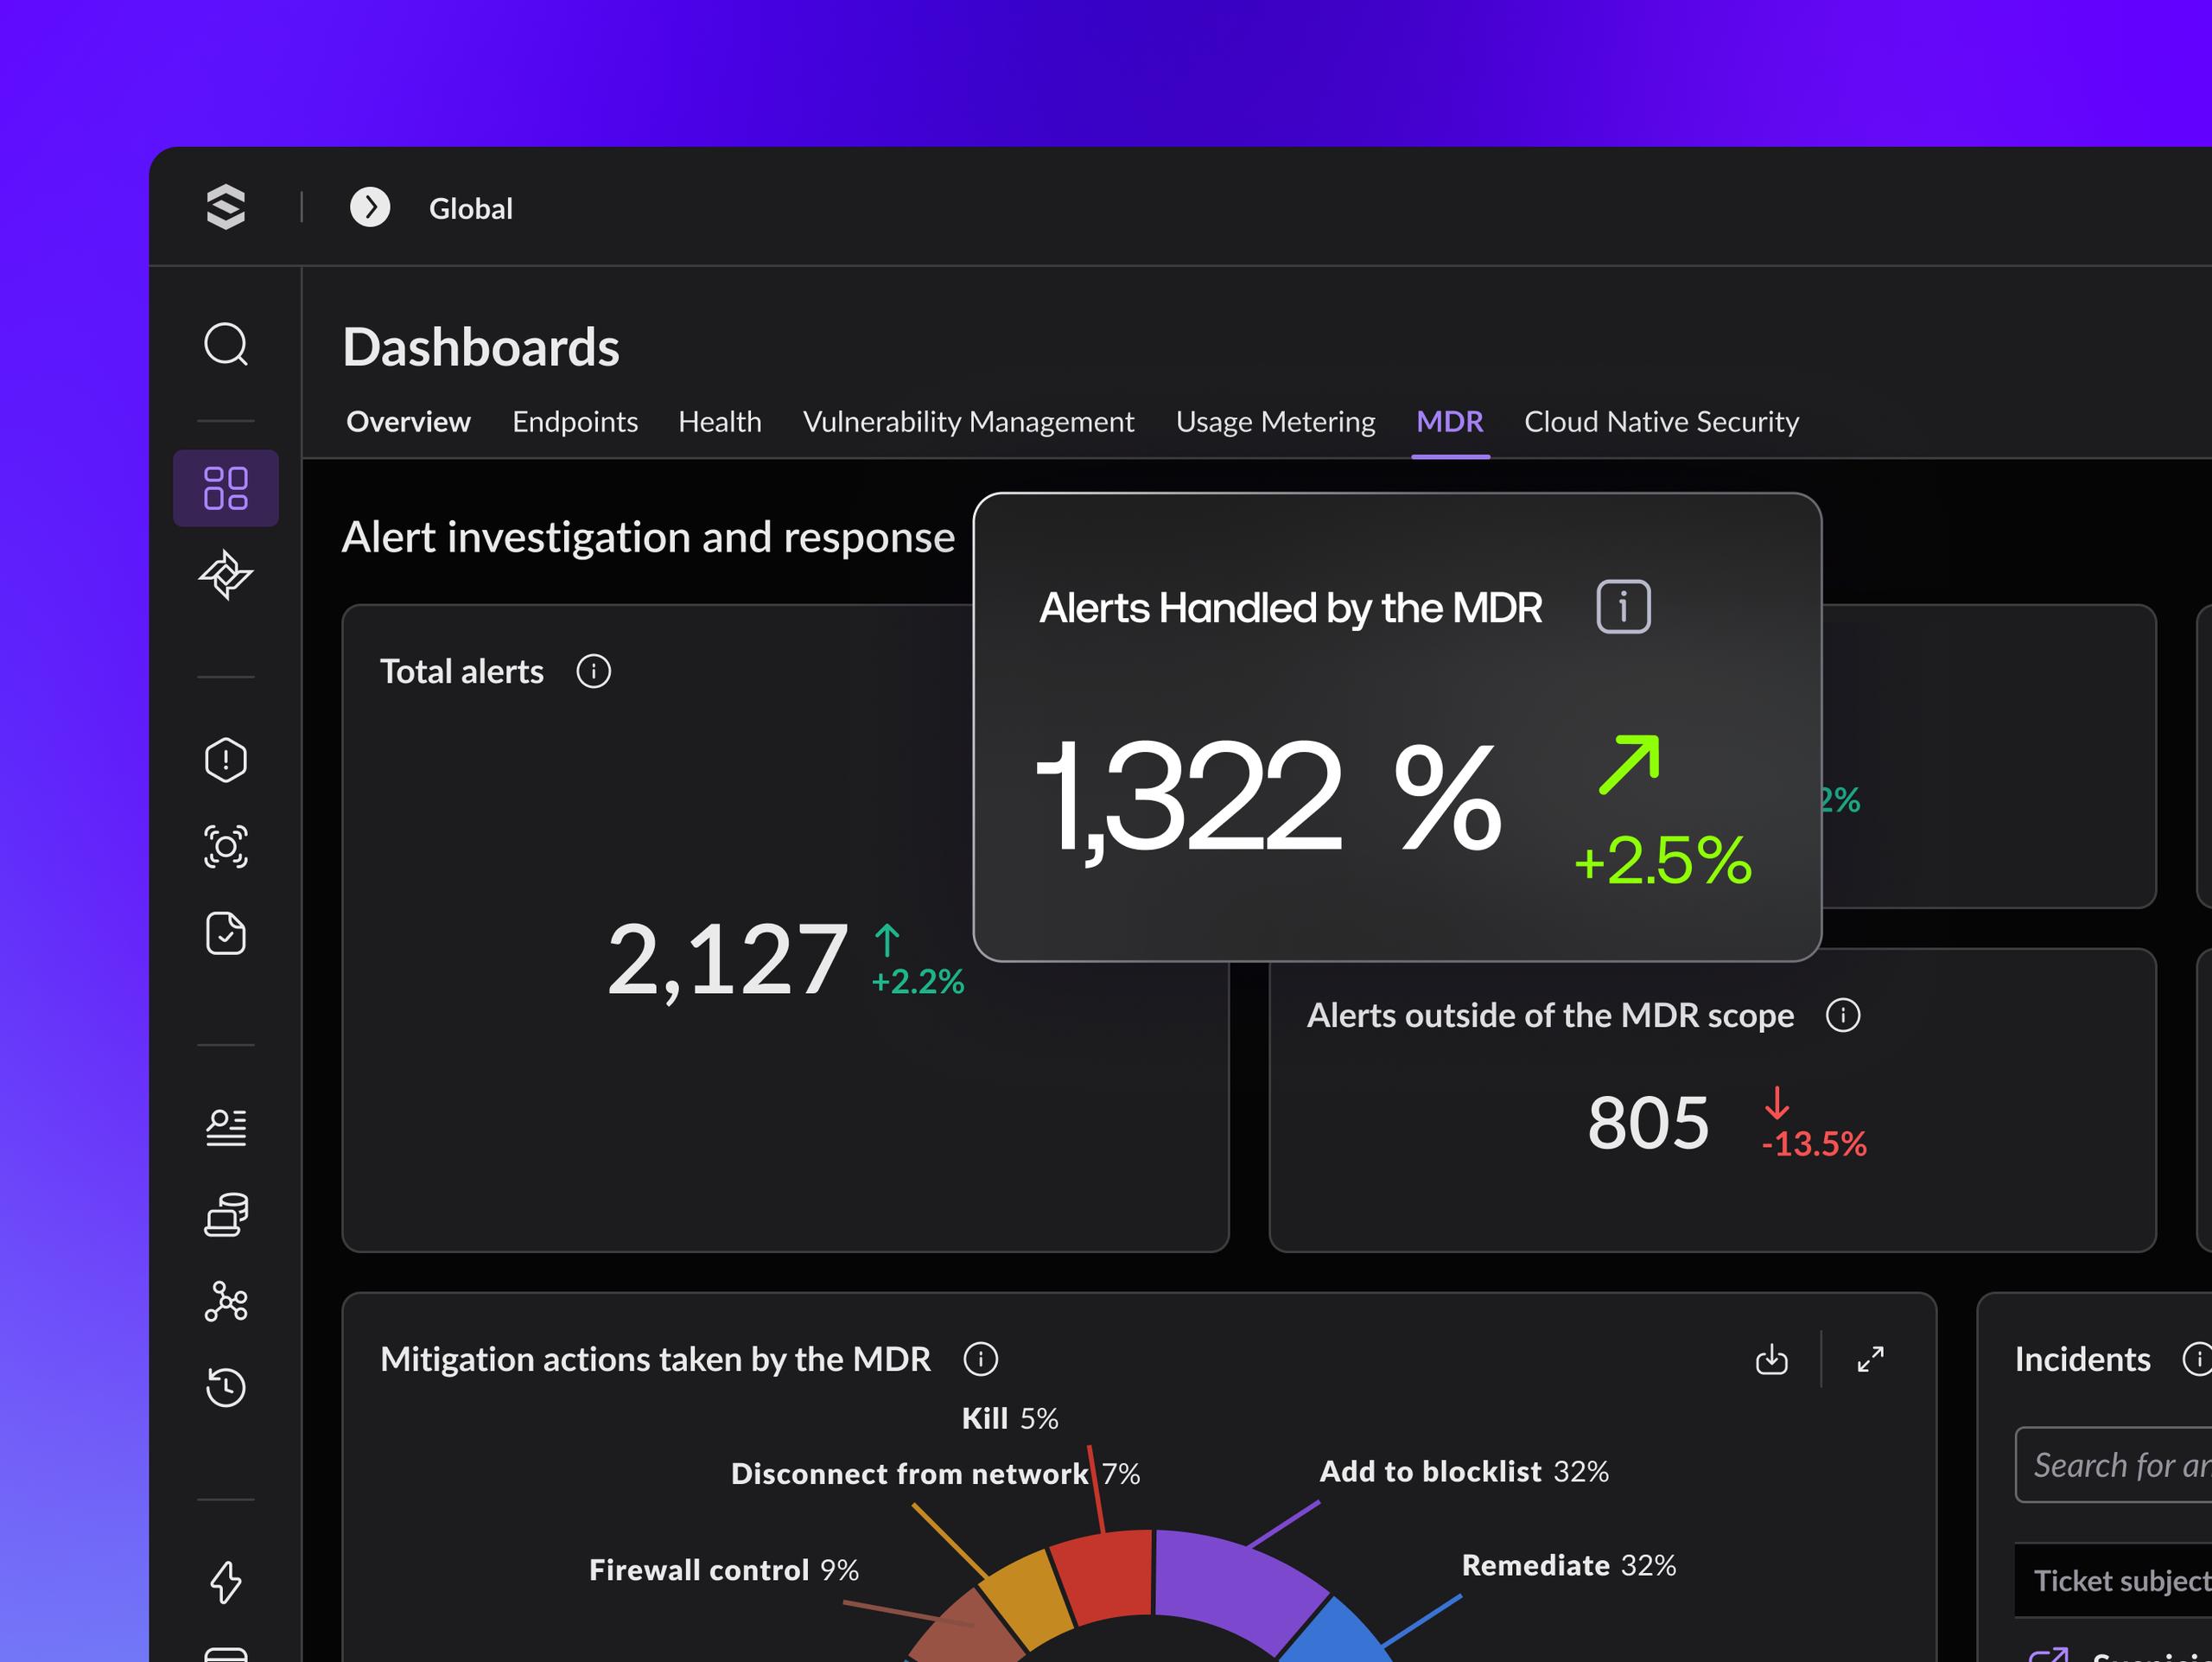
Dark MDR security dashboard with tabs and cards: Total alerts 2,127, Alerts handled 1,322, outside scope 805, plus mitigation actions chart

Experience Greater Efficiency and Coverage with Singularity MDR

Singularity MDR delivers broader detection and response coverage tailored to your organization’s unique needs. Get expert-led threat hunting and 24/7 coverage across endpoints, identities, cloud workloads, and more. Leverage tailored services integration and on-going advisory with our Threat Services Advisors.

Industry Recognition

The Standard in Security Excellence

Tried and trusted by the industry's leading authorities, analysts, and associations.
Dark navy rounded rectangle with white Gartner wordmark and small ® registered trademark symbol

Un Leader. Sei anni consecutivi.

Per il sesto anno consecutivo, SentinelOne è stata nominata Leader nel Gartner® Magic Quadrant™ 2026 per le piattaforme di protezione degli endpoint.


Leggi il report
Burnt-orange background with large white text “MITRE | ATT&CK” and a small ® symbol above the final K

Record-Breaking ATT&CKⓇ Evaluation

SentinelOne has once again proven its industry-leading capabilities in defense in the MITRE ATT&CKⓇ Enterprise Evaluation 2024.


See the Results
Gartner logo on dark navy rounded rectangle with “Peer Insights” in white and light blue, including small trademark symbols

La suite di sicurezza cloud più premiata del settore

SentinelOne è stata riconosciuta come Customers' Choice nell'edizione inaugurale di Gartner® Peer Insights™ 'Voice of the Customer' per le Cloud-Native Application Protection Platforms.


Leggi di più

Trusted by

NVIDIA
Cisco Systems Inc
Motorola Solutions
Mastercard
S&P Global Ltd
Moody's
Abbott Laboratories
Lockheed Martin Corporation
Warner Bros. Discovery, Inc.
DoorDash
Macy's, Inc.
Ace Hardware
Southern Company
Dominion Energy
Occidental Petroleum
AT&T
Norfolk Southern
CSX Corporation
Aston Martin
Warriors

Related Resources

Need Answers?

Frequently Asked Questions

SentinelOne Singularity is an enterprise cybersecurity platform which offers unified prevention, detection, and response across a security estate. Singularity simplifies modern endpoint, cloud, and identity protection through one centralized, autonomous platform for enterprise cybersecurity. SentinelOne Singularity makes machine-speed decisions against threats on the front lines, equipping every endpoint and workload—no matter their location or connectivity—to respond intelligently with powerful static and behavioral AI.

With the Singularity platform, modern enterprises gain the visibility, analytics, and AI-driven automation they need to protect against known and unknown cyber threats, detect and hunt malicious actors, and remediate endpoints at machine speed, without human intervention.

Yes. Singularity Cloud Funnel enables customers to replicate their data to their customer-owned SIEM/log analytics solution, Amazon S3, or Google Cloud Storage buckets.

Singularity Complete delivers AI-powered endpoint and cloud security. It’s designed for customers seeking enterprise-wide protection, detection, and response capabilities, augmented by the intelligence and speed of advanced AI. Singularity Complete includes all Core and Control features.

Singularity Core is the foundation of all SentinelOne endpoint security offerings to replace legacy AV or NGAV with a more effective and easily managed EPP. Core includes static and behavioral AI engines to detect a wide range of attacks.

SentinelOne enables effective threat hunting with an industry leading data retention of 365 days out of the box for malware and fileless attack incidents. We offer 14 days standard historical EDR data retention with an affordable option to upgrade to 365 days.

Singularity Complete delivers AI-powered endpoint and cloud security. It’s designed for customers seeking enterprise-wide protection, detection, and response capabilities, augmented by the intelligence and speed of advanced AI. Singularity Complete includes all Core and Control features.

Singularity Control includes all Core features plus additional security suite features such as Firewall Control, Device Control, and more.

The SentinelOne Singularity platform intelligently automates EDR and XDR by providing Storyline context and a full range of automated and manual remediation actions. The Singularity platform distills robust, continuous telemetry into the most actionable insights and response actions for analysts, as demonstrated consistently in the MITRE Engenuity ATT&CK® Evaluations.  Devices defend themselves autonomously by killing and quarantining unauthorized processes and files in real-time. Devices also heal themselves with surgical, automated remediation and rollback to help reduce Mean Time to Remediate (MTTR). Threat hunters and incident responders can also use these functions to mark identified suspicious situations as threats for automatic, estate-wide remediation which greatly increases responder efficiency.

Yes, SentinelOne supports threat hunting using MITRE ATT&CK Tactics, Techniques, and Procedures (TTPs), the behavioral indicators mapped by the MITRE ATT&CK framework, to help analysts understand endpoints’ behavior and accurately detect and respond to any anomalous activity. This feature helps uplevel analysts’ skills and context and makes the EDR user experience more satisfying and efficient from day one.

With increasingly complex security architectures, limited resources, and more sophisticated attacks, security teams can often struggle to stay ahead of threats. Singularity Complete uses AI to assist overstretched teams with correlated, summarized, and actionable guidance to help analysts during hunting and investigation, so your team spends less time manually chasing threats and more time focused on strategic initiatives.

Decorative background gradient

Scopri la piattaforma di cybersecurity più avanzata

Scopri come la piattaforma di cybersecurity autonoma e più intelligente al mondo può proteggere la tua organizzazione oggi e in futuro.
Dark dashboard UI with purple-highlighted nav, summary cards showing 149, 7, 78, 56, 1.2 h, and a status table with linked purple text