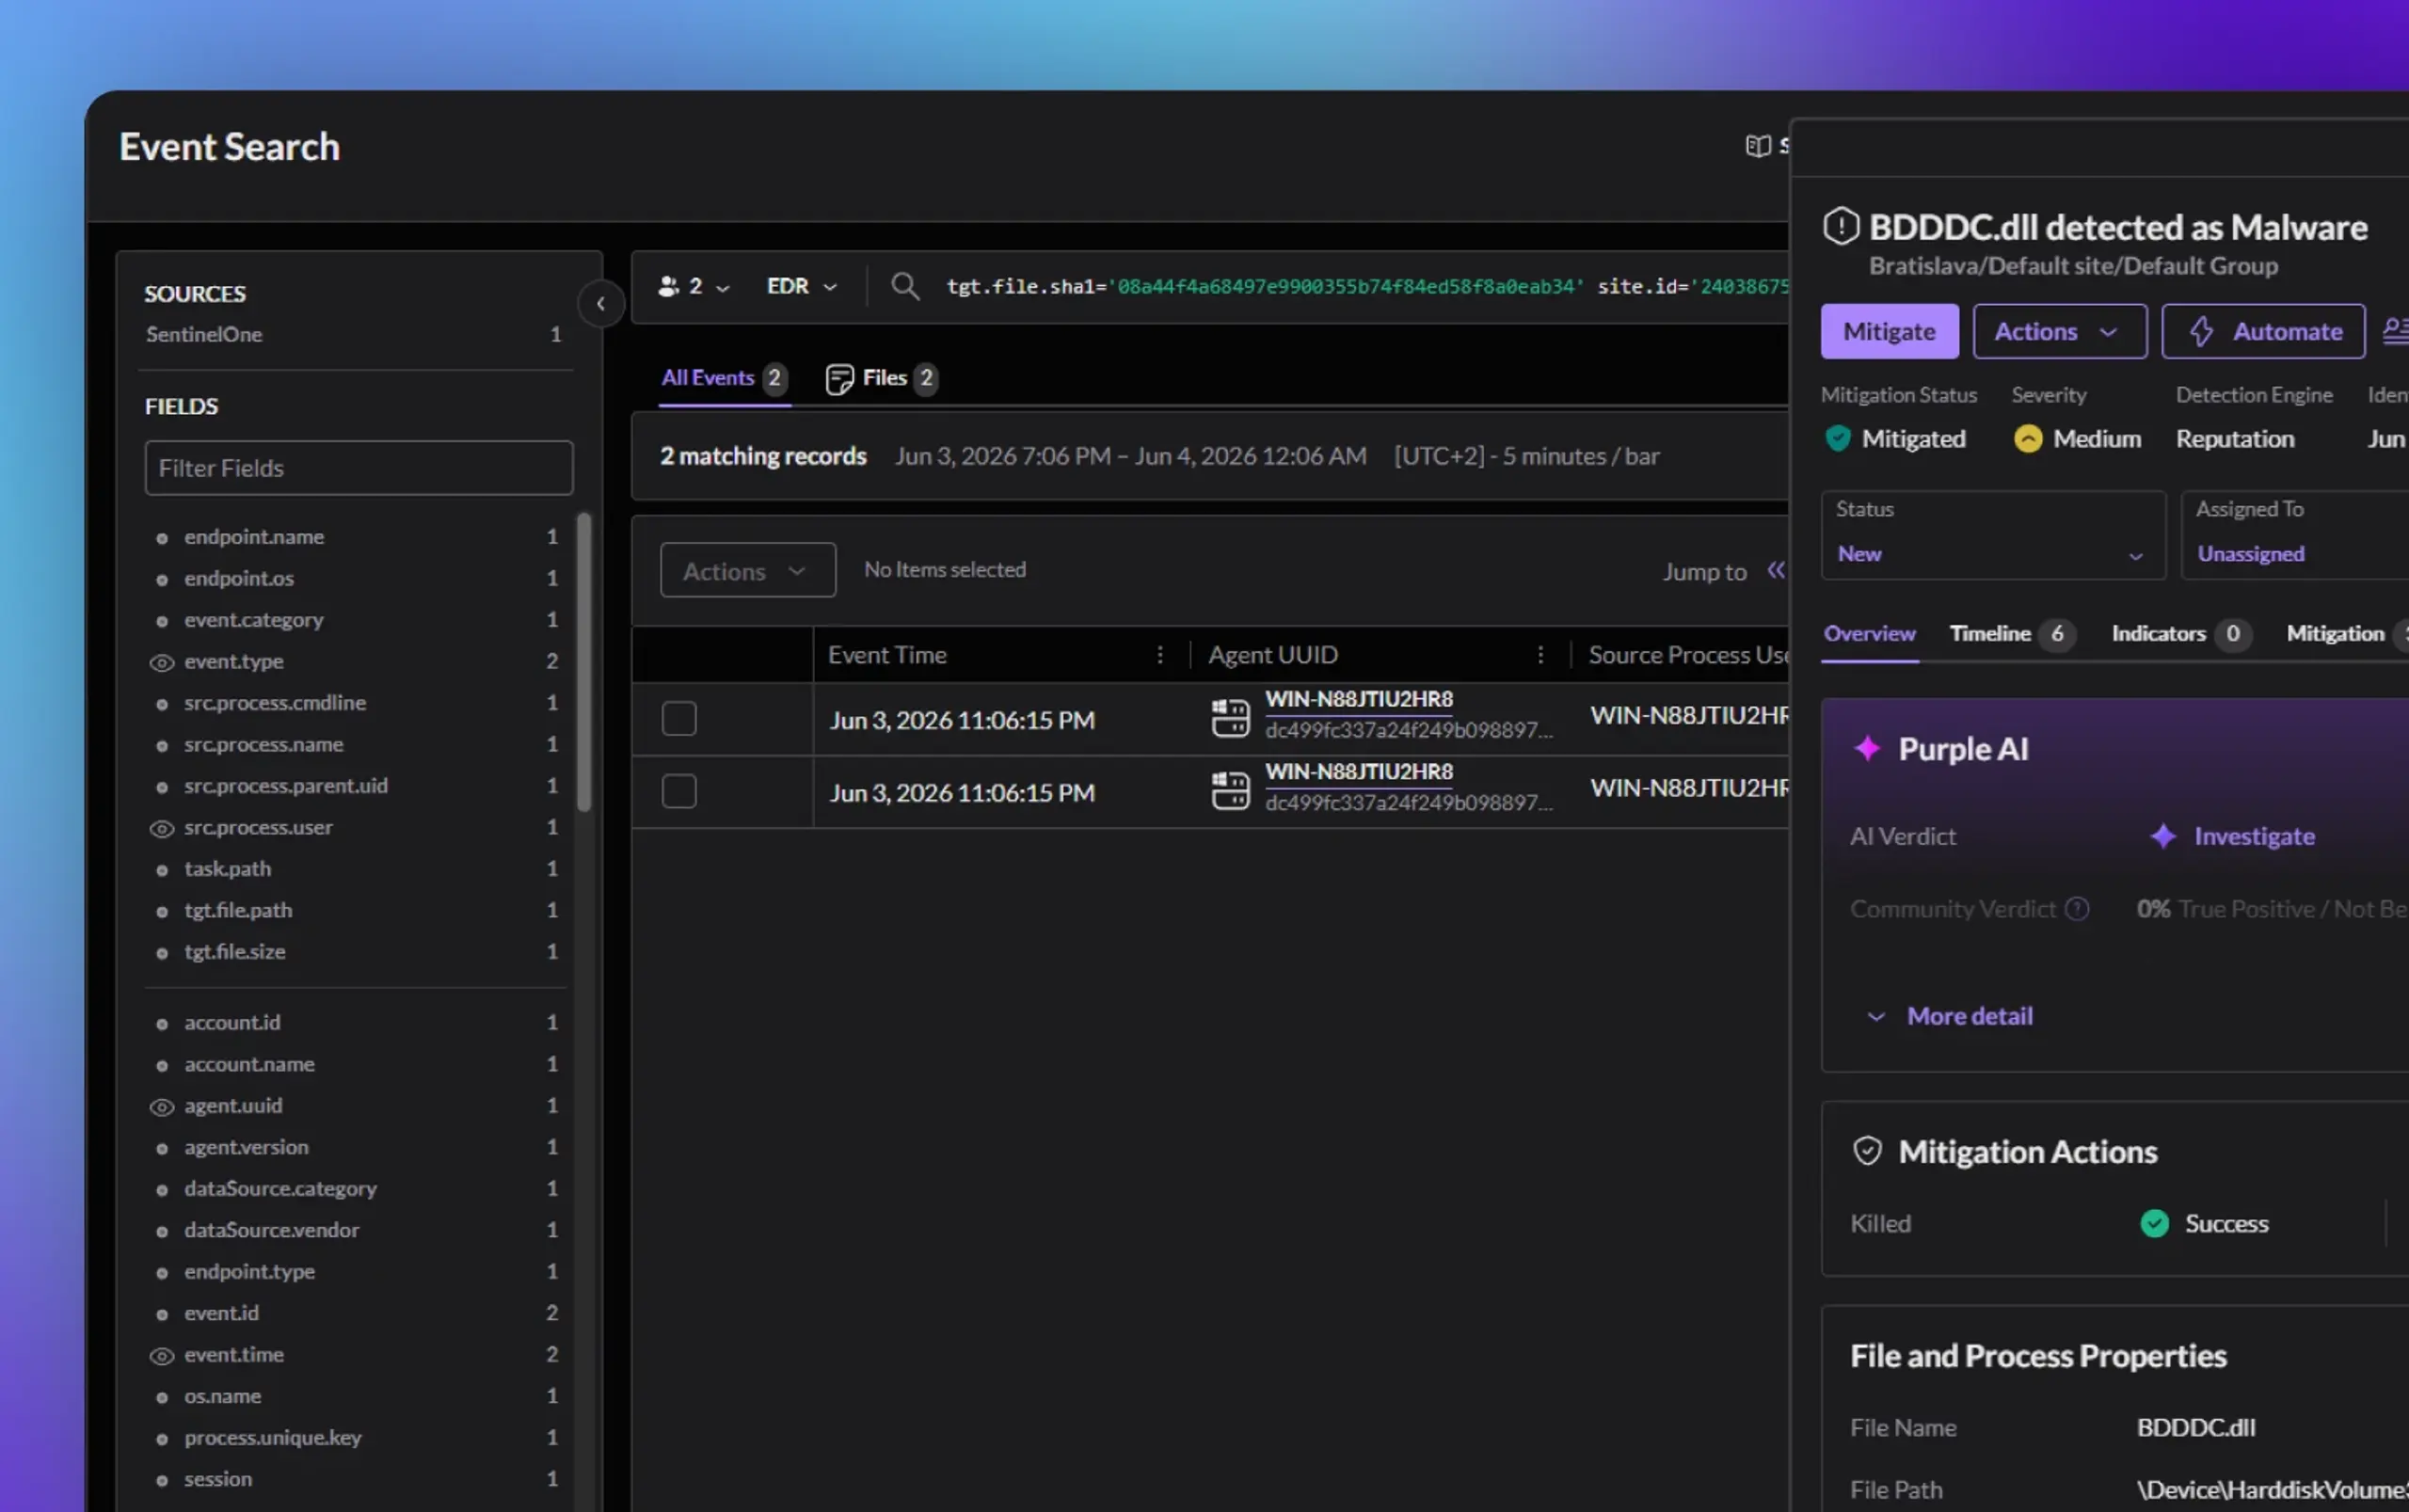
Singularity™ Application Control

Stop Unauthorized Software
Before It Runs

Singularity Application Control decides what's allowed to execute on every managed endpoint, blocking ransomware and unapproved software before they run. No new agent required.

O-02-secondary-hero-50-50-application-control.webp

Today's Reality

01
M-11-immersive-application-control-platform-illustration-01.webp

Prevention

Zero Trust, Applied to Execution.

Nothing is trusted to run by default. Policy-based allowlisting blocks unauthorized applications before they execute. Blocklisting adds a second layer against known bad software.

  • Block execution by publisher, path, hash, or process

  • Combine allowlisting and blocklisting in a single policy

  • Catch living-off-the-land techniques like launching PowerShell from Word
02
M-11-immersive-application-control-platform-illustration-02.webp

Deployment

No New Agent. No New Console.

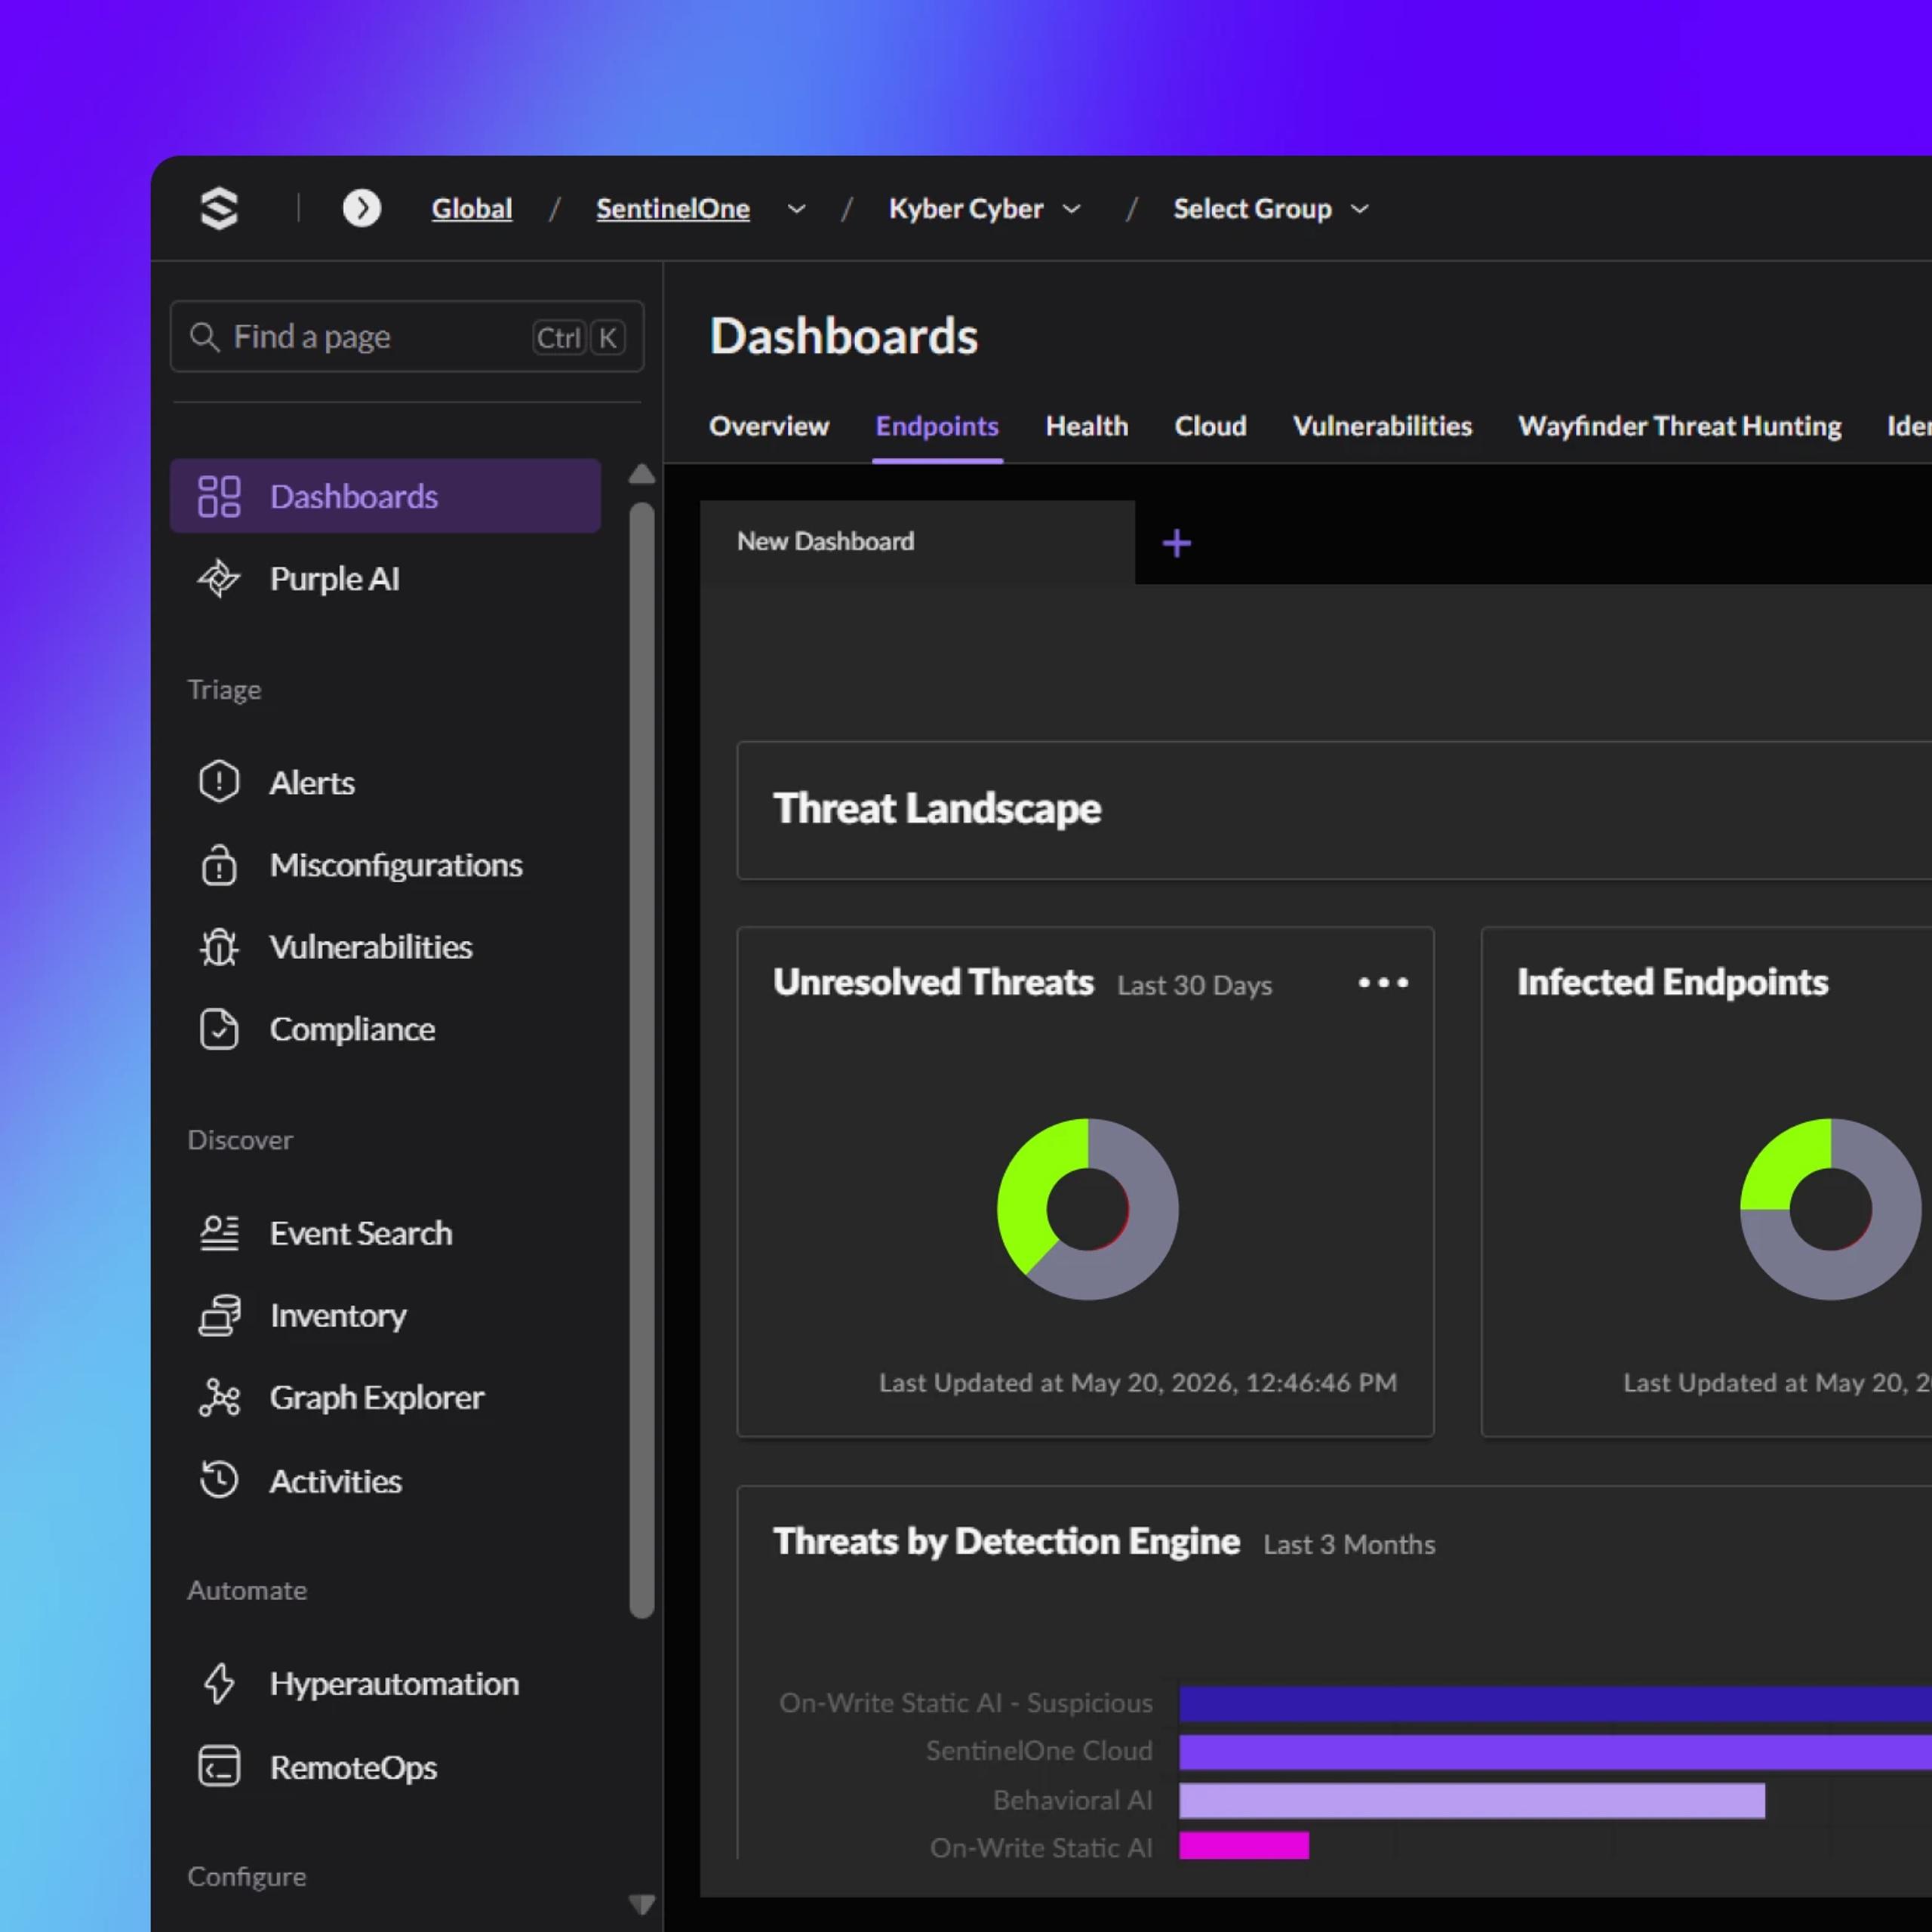
Application Control runs inside the SentinelOne agent you already have deployed. No separate tool. No second console to log into.

  • Zero additional infrastructure to stand up

  • Policy and telemetry live in the console your team already uses

  • Bulk rule import via CSV for enterprise-scale rollout

03
M-11-immersive-application-control-platform-illustration-03.webp

Validation

Verify First. Enforce with Confidence.

Monitor mode is Zero Trust applied safely. Teams see exactly what would be blocked before a single rule goes live.

  • Audit impact before enforcing, with no risk to production apps

  • Every process-creation event gets a verdict, even in monitor mode

  • Default allowlist covers core OS and SentinelOne binaries out of the box

04
M-11-immersive-application-control-platform-illustration-04.webp

Resilience

Built for Systems That Can’t Afford Surprises

Purpose-built for OT, fixed-function, and compliance-mandated environments where traditional EDR wasn't designed to enforce lockdown.

  • Locks critical systems to their intended function so nothing else runs

  • Supports the allowlisting control required by CMMC, NIST, and the ASD Essential Eight

  • Logs every rule change with who made it and when

Decorative background gradient

Get Started

Abstract glossy 3D knot of interwoven translucent ribbon loops in iridescent blue, purple, pink, and cyan on white

Use Cases

Your Endpoints. Your Rules.

One Console Instead of Two

Drop the legacy allowlisting tool and its second console without losing the control that kept it around.

O-15-image-card-grid-application-control-illustration.webp

The Two-Console Tax

Keep the allowlisting your team relies on, without paying for a second agent and console.

O-15-image-card-grid-application-control-block-ransomware.webp

One Console for Renewal Decisions

See what’s actually enforced on the endpoint before the renewal conversation, not after an incident.

Results

Proof, Not Promises.

Application Control runs on the same Singularity Platform that analysts and evaluations rank among the best for endpoint protection and detection accuracy.
  1. 01

    0%

    Detection accuracy in MITRE ATT&CK® Evaluations, with 88% less noise than median

    O-26-proof-card-grid-slotlogo-mitre.svg
  2. 02

    0 Years

    Named a Leader in the 2026 Gartner® Magic Quadrant™ for Endpoint Protection

    Rounded square logo with dark navy background and bold white “Gartner” text plus a small “®” symbol
  3. 03

    0%

    Would recommend for EDR and EPP on Gartner® Peer Insights™

    Gartner logo on dark navy rounded rectangle with “Peer Insights” in white and light blue, including small trademark symbols

Success Stories

Trusted When It Matters Most

Arena scoreboard reading “CHASE CENTER” above a video screen of three people; crowd and pyrotechnic smoke jets rise

"예방, 탐지 및 대응을 위한 SentinelOne의 단일 플랫폼은 우리에게 판도를 바꾸는 역할을 했습니다. 위협을 실시간으로 모니터링할 수 있는 중앙 집중식 시스템을 갖춤으로써 귀중한 시간과 리소스를 절약할 수 있었습니다."

Brian Fulmer

Senior Director of IT at Golden State Warriors

스토리 읽기
Close-up of a teal F1 race car cockpit and side body with “BOSS,” “aramco,” “SentinelOne,” “BOMBARDIER,” and “ASTON MA…” branding

“모든 데이터를 하나의 플랫폼에 보유하고 있어 이를 신속하게 분석하고 의사 결정을 내릴 수 있다는 사실은 우리에게 진정한 게임 체인저입니다.”

Mark Carter

Chief Architect & Cybersecurity Officer at Aston Martin Aramco Formula One

스토리 읽기
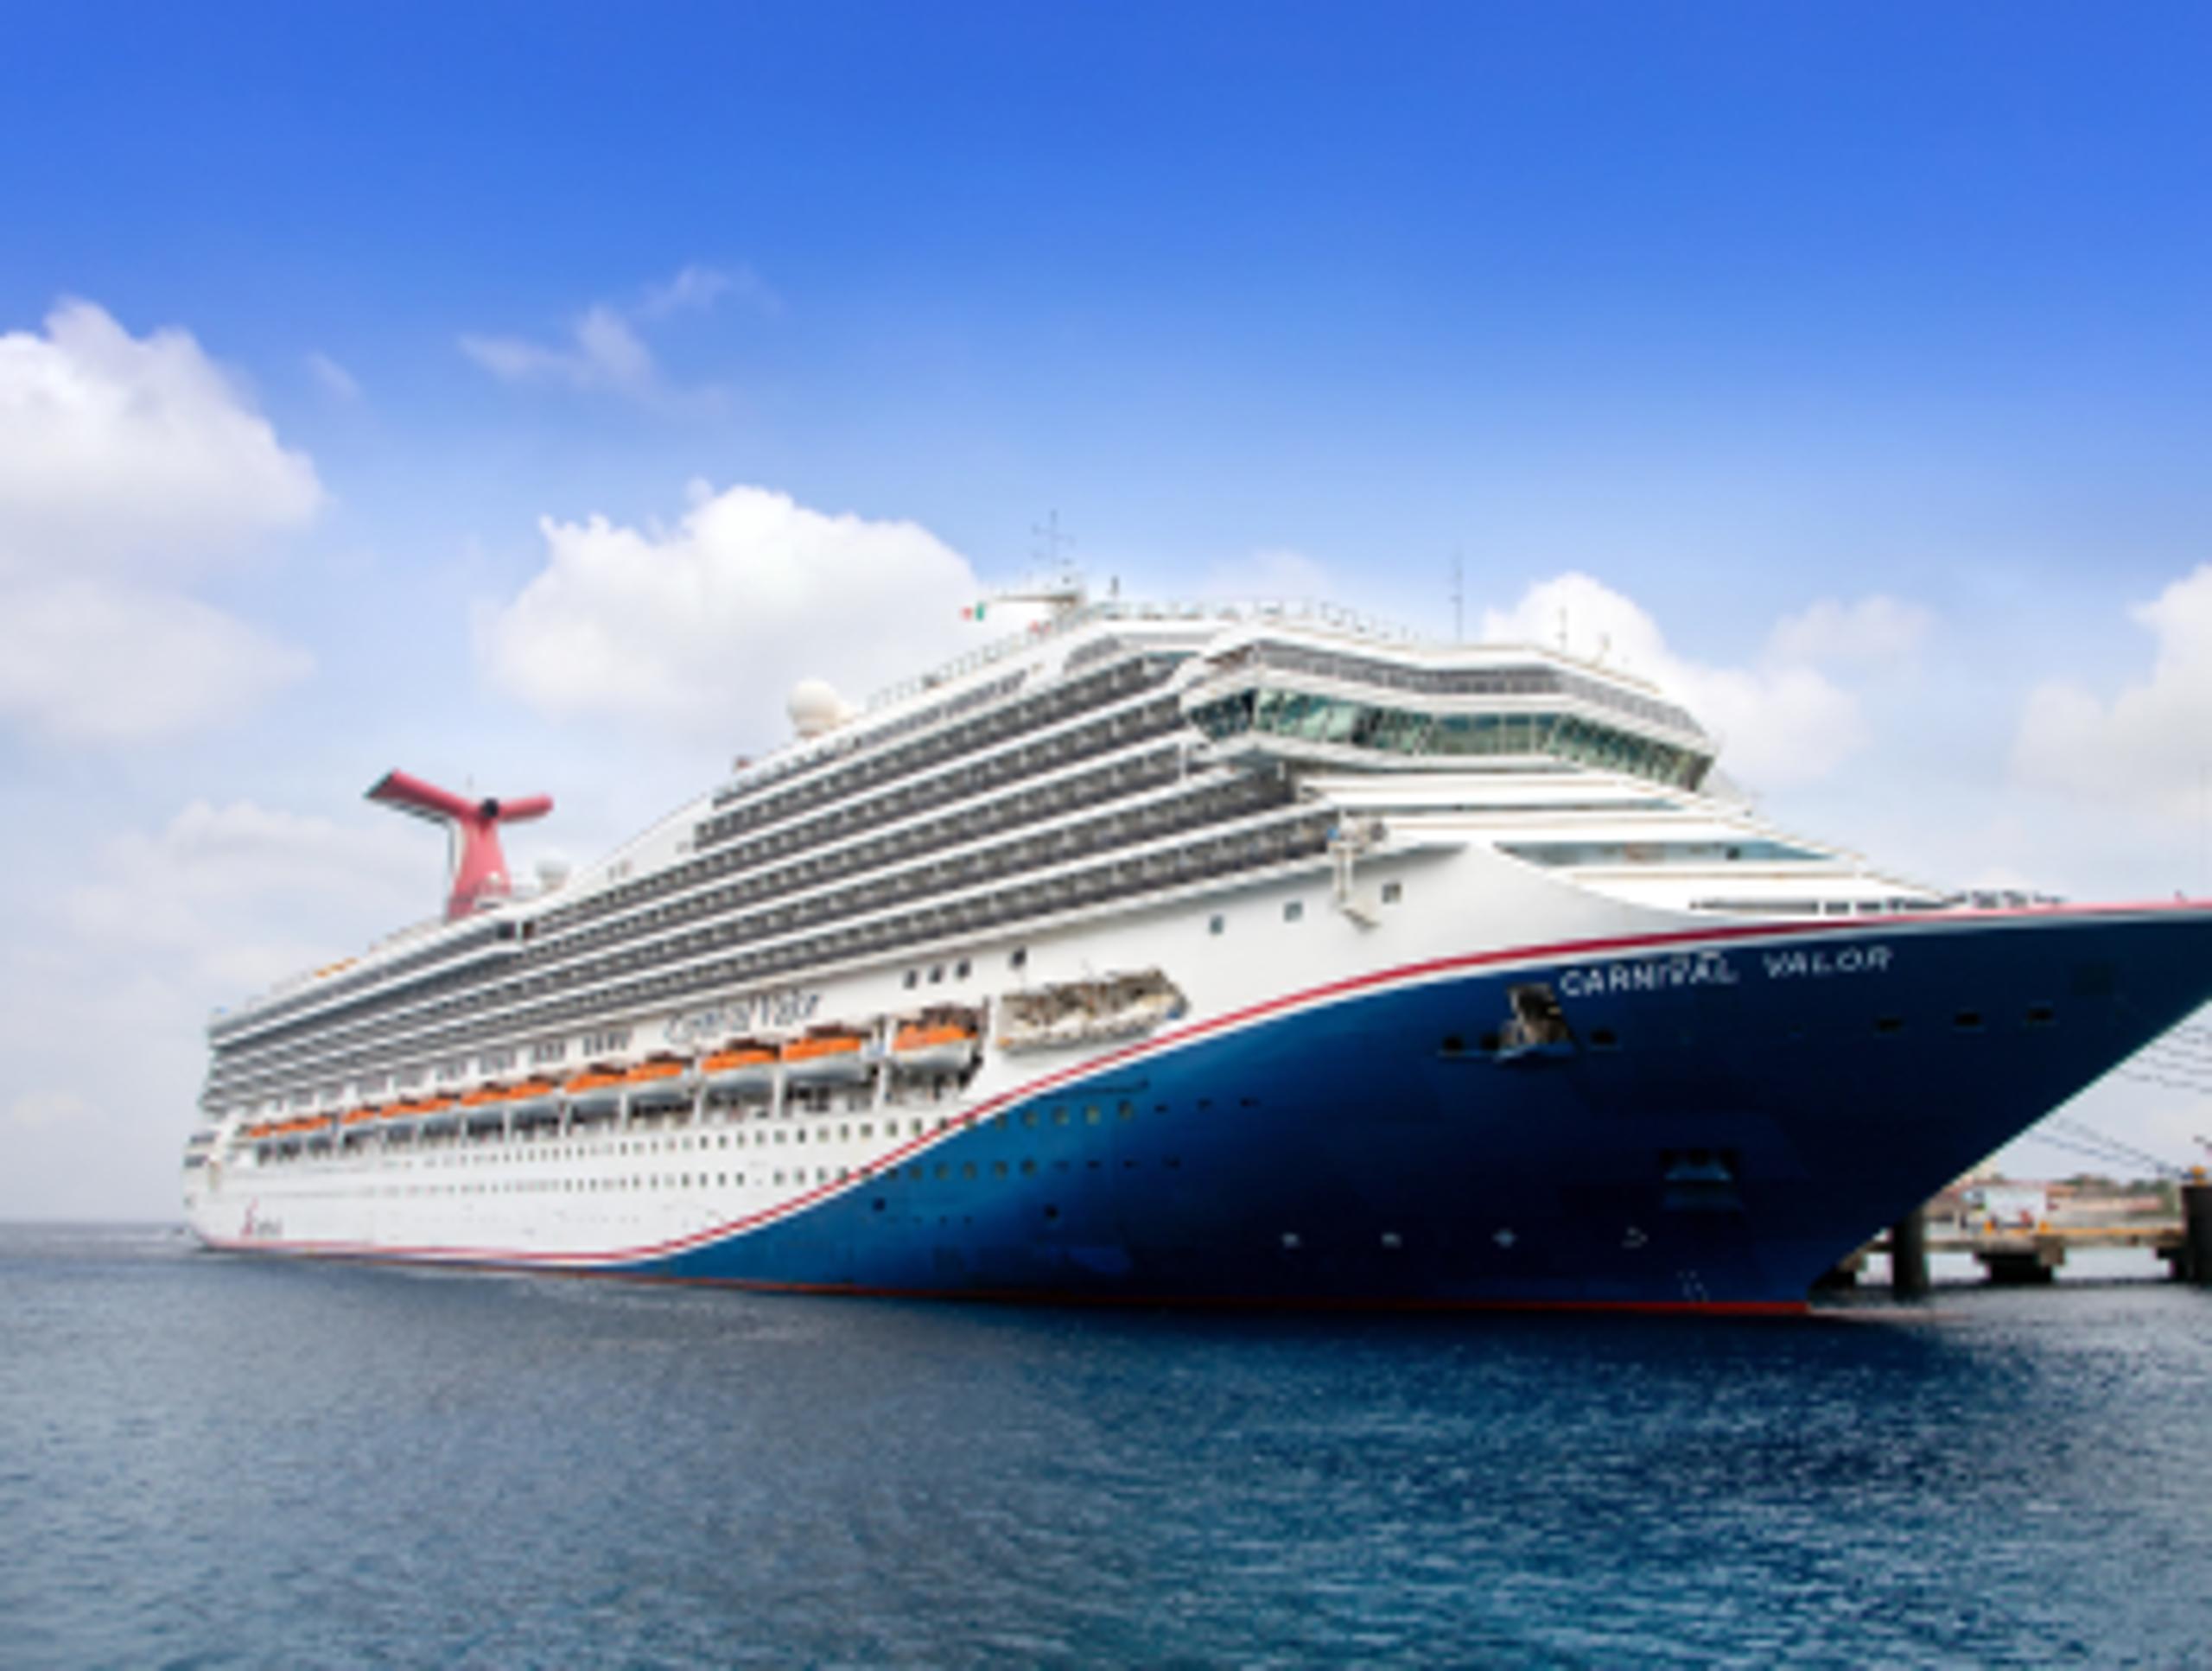
Cruise ship in harbor with sign CARNIVAL VICTORY on the bow, blue water ripples, lifeboats, and red funnel

“SentinelOne caught an incident that every other tool missed. That gave us confidence.”

Alex Tabares

Associate Vice President, Threat Management and Intel at Carnival Corporation

Read the Story

Why SentinelOne?

Your Enforcement Advantage

The capabilities that set Singularity Application Control apart from standalone allowlisting tools.
O-15-image-card-grid-application-control-brand-image-render-glass-tech-grid-tiles.webp

One Console for Every Endpoint Event

Policy, decisions, and telemetry live in the same console as every other endpoint event. No second console for allowlisting.

O-15-image-card-grid-application-control-brand-image-office-work-laptop.webp

Monitor Before You Enforce

See what would be blocked before a rule goes live, and catch problems before they reach production.

O-15-image-card-grid-application-control-forensics-brand-image-render-glass.webp

Built for Fixed-Function and Regulated Systems

Granular controls by publisher, path, hash, or process, combined however you need, for the systems that can least afford a mistake.

Platform Integration

One Agent. Every Verdict.

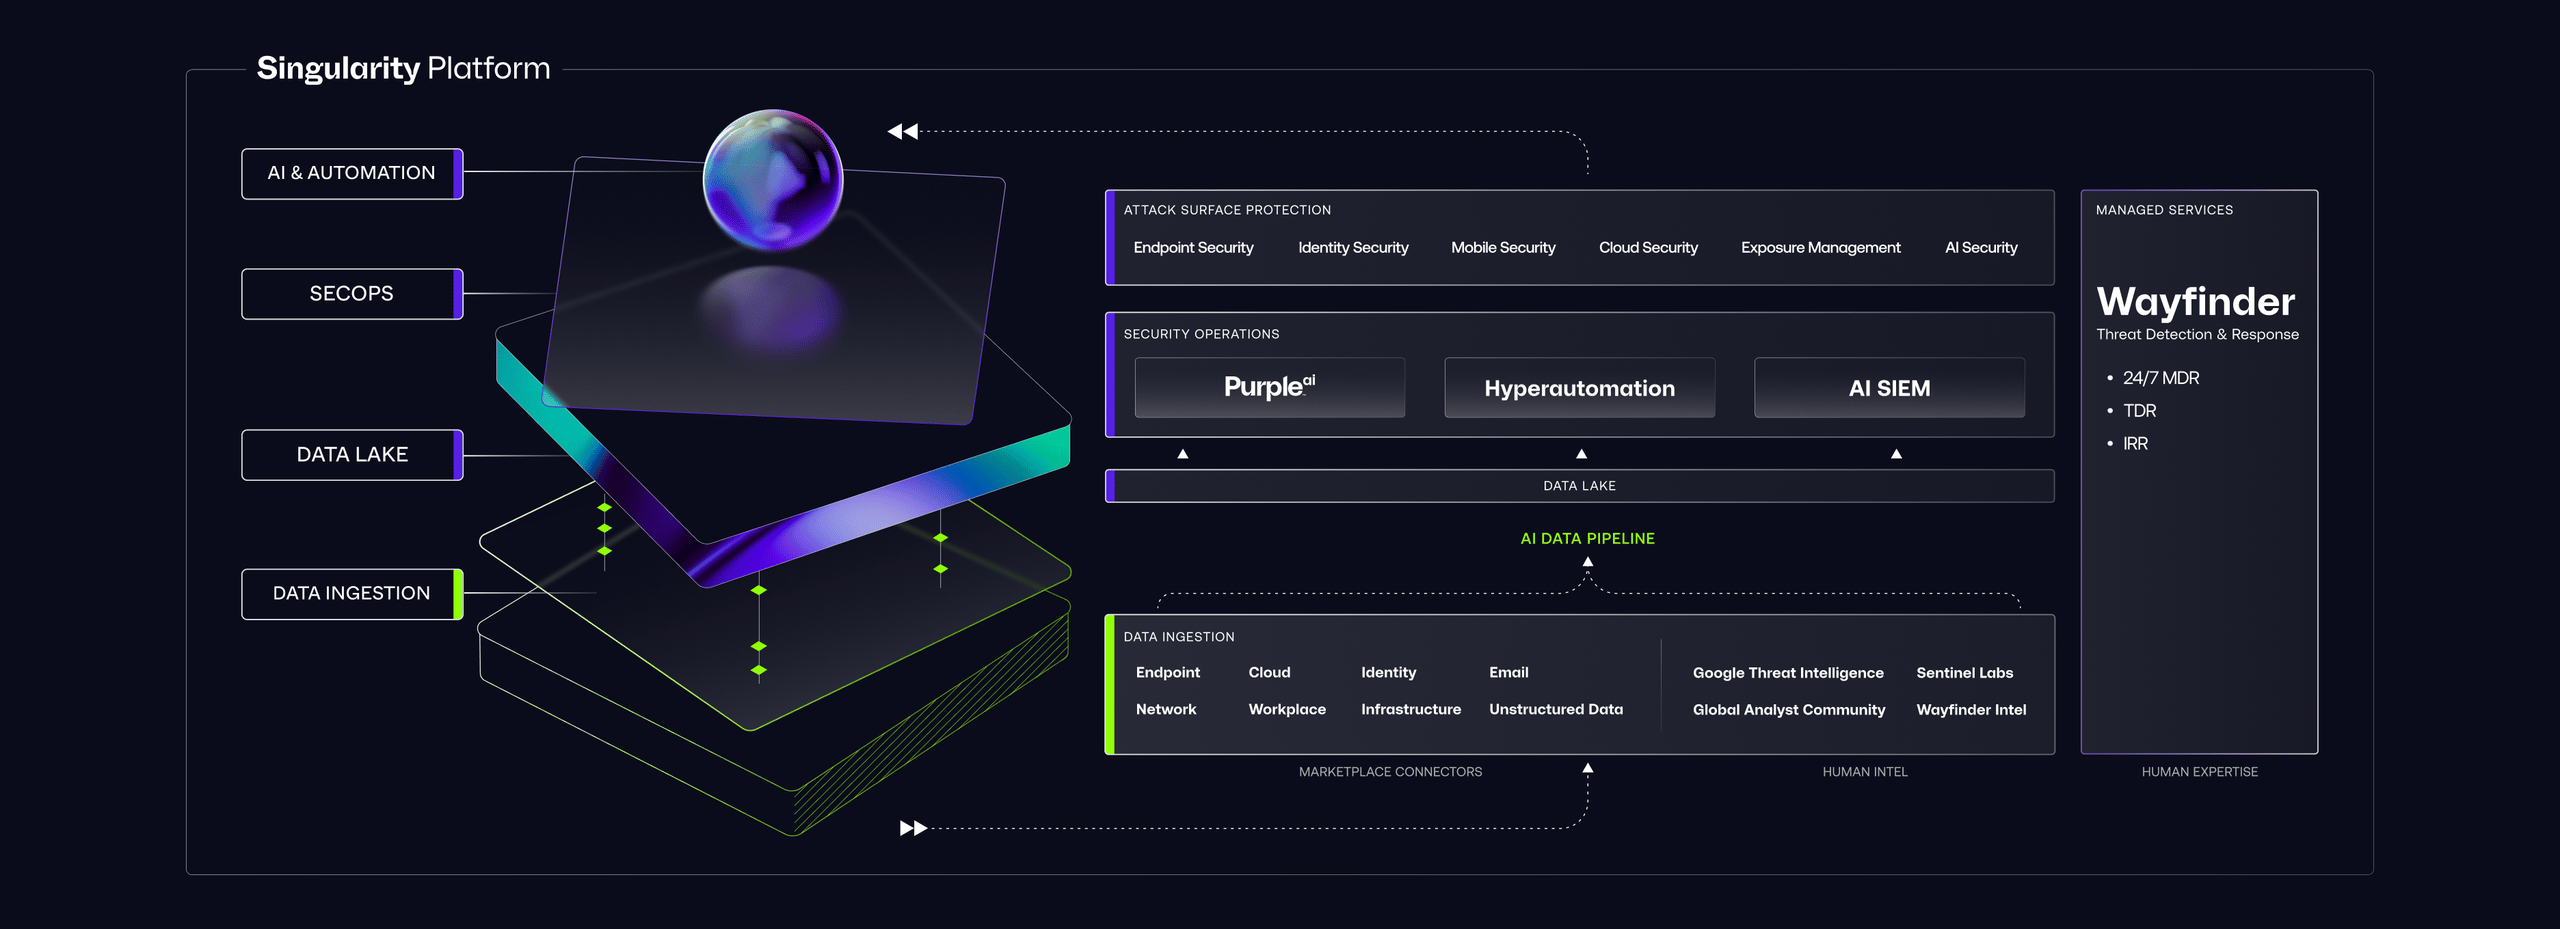
Futuristic UI mockup titled “Singularity Platform” with neon platform, orb, labeled sections, and sidebar “Wayfinder”
01

Singularity Endpoint

Application Control runs inside the same agent and console as EDR. Enforcement and detection telemetry stay unified, no exporting data or switching tools.

02

Deep Visibility

Every allowed, monitored, and blocked decision lands in the same process-creation timeline as every other endpoint event.

03

Singularity Platform

One platform unifying security data across endpoints, cloud, and identity. Application Control's enforcement data feeds into that same unified view.

Resources

Go Deeper on Application Control

Need Answers?

Frequently Asked Questions

Application control is a security capability that decides which applications are allowed to run on an endpoint. Singularity Application Control enforces that decision through policy-based allowlisting and blocklisting, built into the existing SentinelOne agent.

No. Application Control activates within your existing Singularity Complete deployment. There is no additional agent to install and no separate console to manage.

Monitor mode reports on application activity without blocking it, so teams can validate policy before enforcing. Allow and Block apply the policy directly once that validation is done.

Decorative background gradient

Next Steps

Put Your Allowlist to Work

Dark dashboard UI with purple-highlighted nav, summary cards showing 149, 7, 78, 56, 1.2 h, and a status table with linked purple text