Back to Blog

Category

From the Front Lines

Keep up with the latest

From the Front Lines Blogs

  • HiveNightmare | Protecting Windows 10 Security Account Manager Against CVE-2021-36934

    HiveNightmare | Protecting Windows 10 Security Account Manager Against CVE-2021-36934

  • CVE-2021-3122 | How We Caught a Threat Actor Exploiting NCR POS Zero Day

    CVE-2021-3122 | How We Caught a Threat Actor Exploiting NCR POS Zero Day

  • PrintNightmare Vulnerability: Analysis and Mitigation

    PrintNightmare Vulnerability: Analysis and Mitigation

  • REvil’s Grand Coup | Abusing Kaseya Managed Services Software for Massive Profits

    REvil’s Grand Coup | Abusing Kaseya Managed Services Software for Massive Profits

  • DarkRadiation | Abusing Bash For Linux and Docker Container Ransomware

    DarkRadiation | Abusing Bash For Linux and Docker Container Ransomware

  • Meet DarkSide and Their Ransomware - SentinelOne Customers Protected

    Meet DarkSide and Their Ransomware - SentinelOne Customers Protected

  • SentinelOne and HAFNIUM / Microsoft Exchange 0-days

    SentinelOne and HAFNIUM / Microsoft Exchange 0-days

  • Stopping SolarWinds Breach with Jared Phipps

    Stopping SolarWinds Breach with Jared Phipps

  • Inside the Mind of the SUNBURST Adversary

    Inside the Mind of the SUNBURST Adversary

  • FireEye/SolarWinds: Taking Action and Staying Protected

    FireEye/SolarWinds: Taking Action and Staying Protected

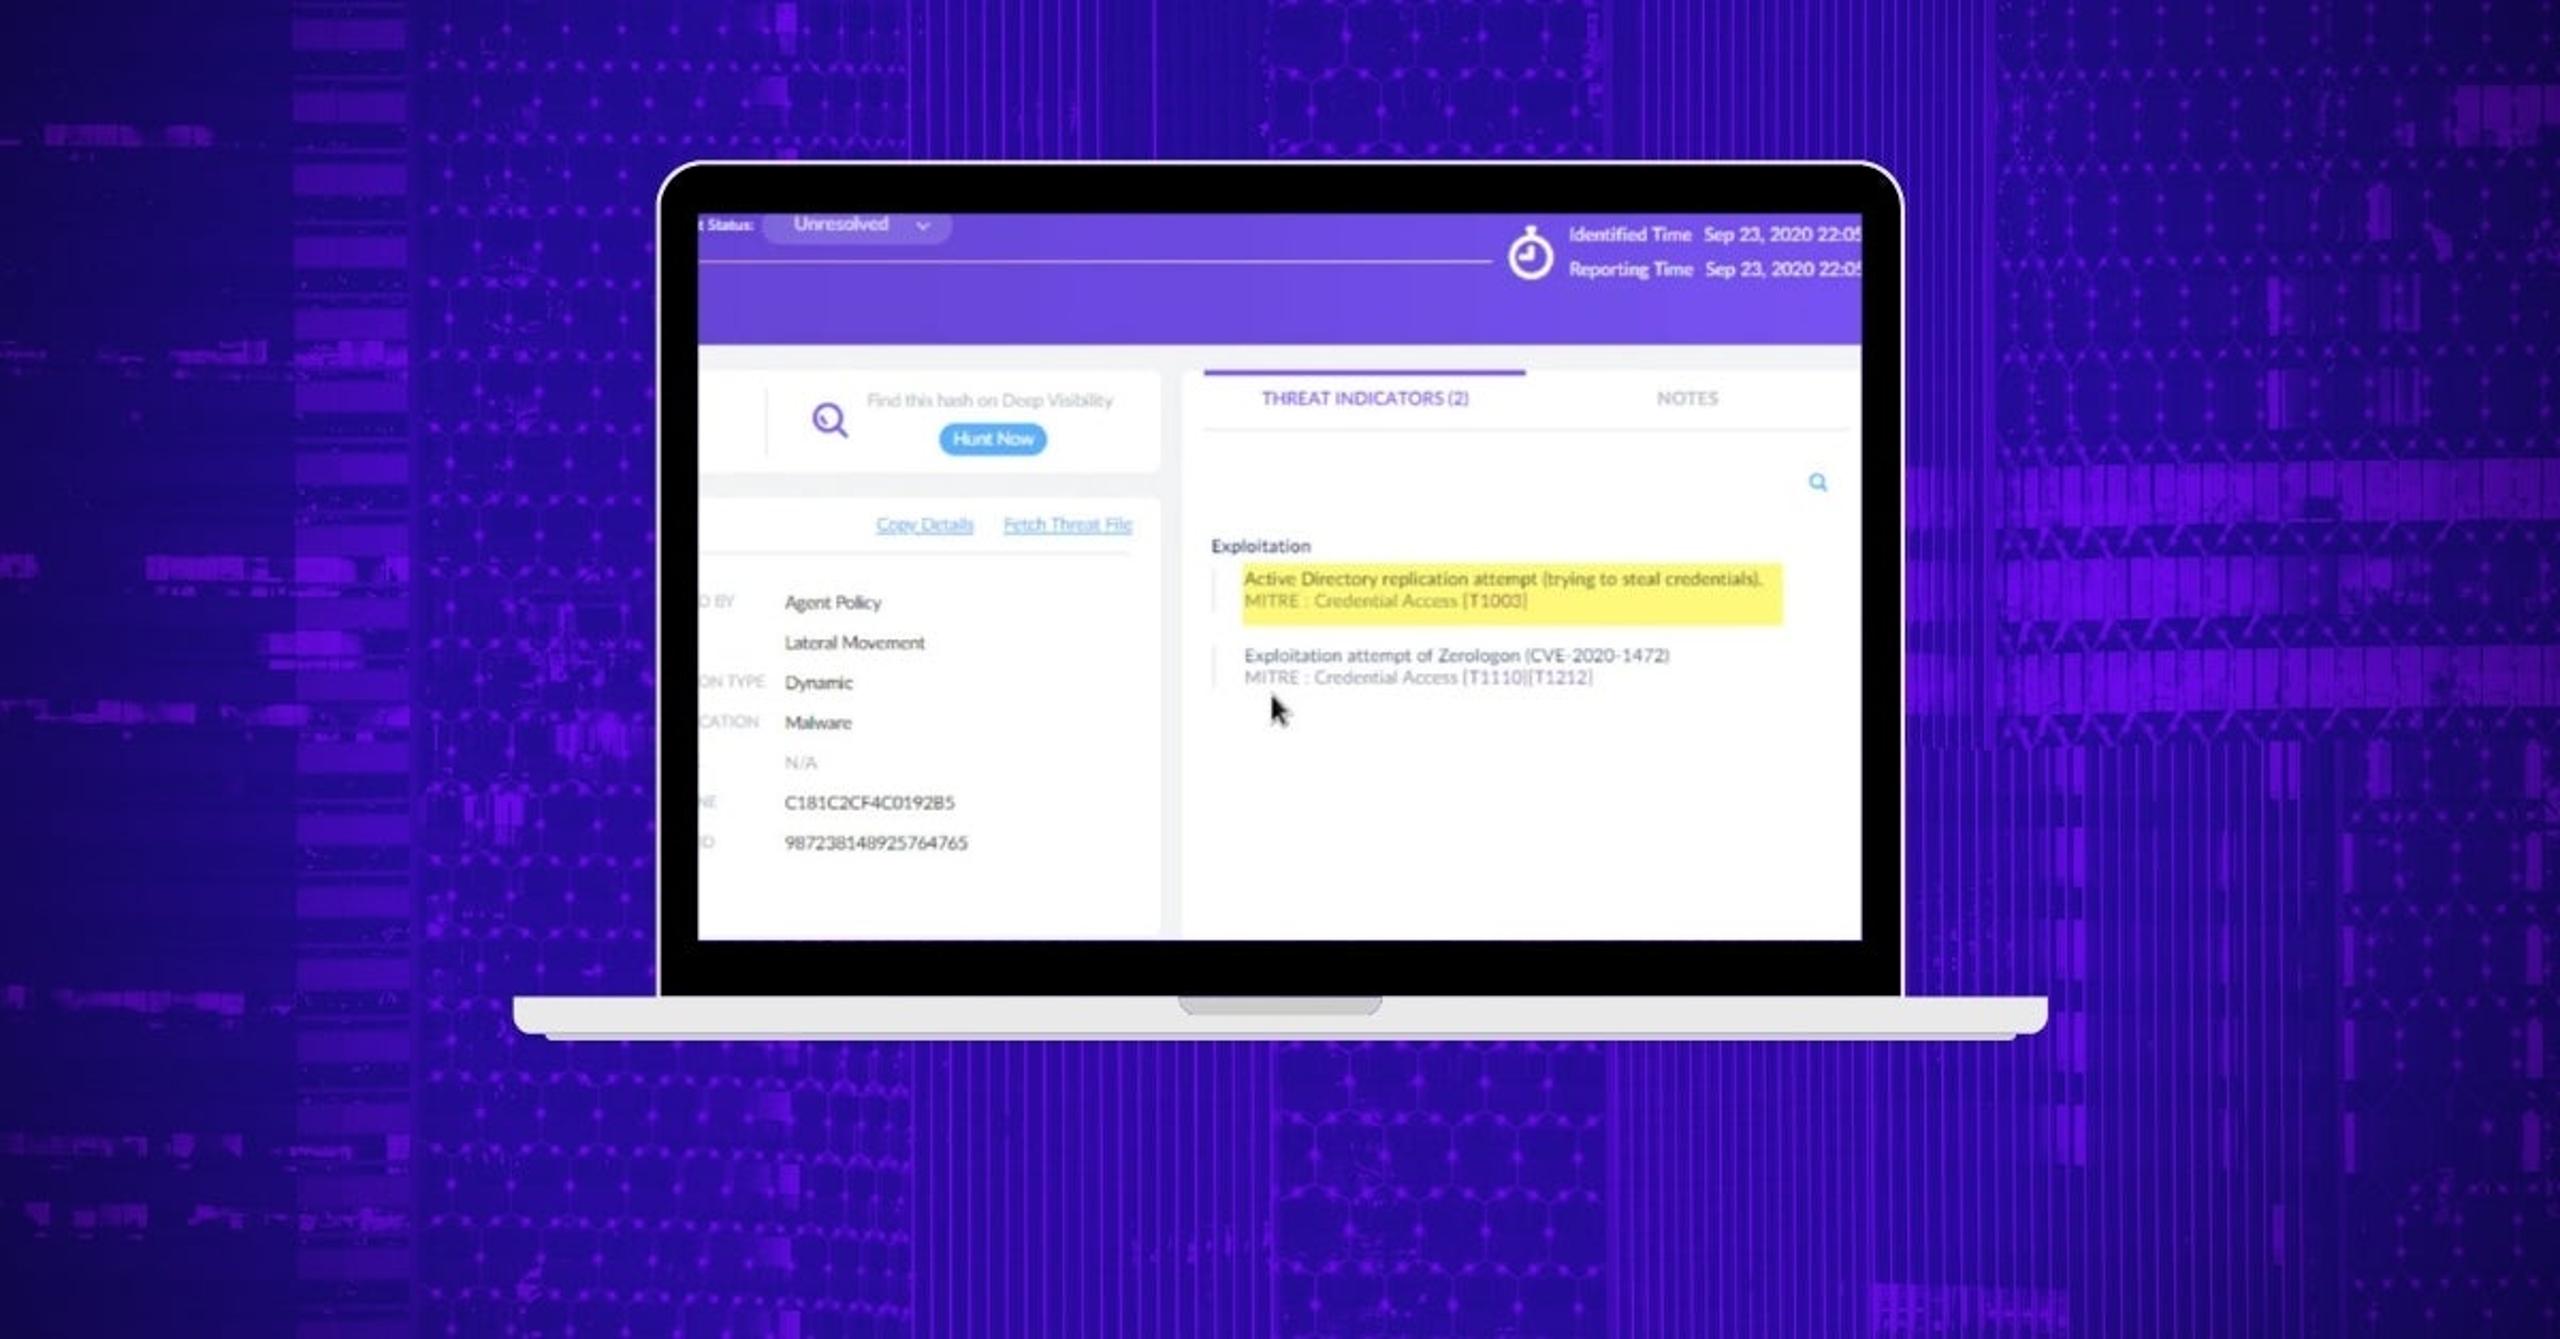
  • CVE-2020-1472: SentinelOne First to Detect Zerologon

    CVE-2020-1472: SentinelOne First to Detect Zerologon

  • The BLINDINGCAN RAT and Malicious North Korean Activity

    The BLINDINGCAN RAT and Malicious North Korean Activity