Decorative background gradient

TRUSTED BY 14K+ CUSTOMERS GLOBALLY

The Endpoint Protection Platform for Every Business

SentinelOne delivers autonomous prevention, detection, and response for teams evaluating endpoint protection software. AI-powered protection stops known and unknown threats before they execute. No manual intervention required.

Let’s Get Started

Schedule a Demo

Trusted by

Applied Materials
NVIDIA
Cisco Systems Inc
Motorola Solutions
Mastercard
S&P Global Ltd
Moody's
Abbott Laboratories
Lockheed Martin Corporation
Warner Bros. Discovery, Inc.
DoorDash
Macy's, Inc.
Ace Hardware
Southern Company
Dominion Energy
Occidental Petroleum
AT&T
Norfolk Southern
CSX Corporation
Aston Martin
Warriors

EPP + EDR. One Agent. Total Coverage.

Most vendors make you choose between prevention and detection. SentinelOne delivers both — plus automated response — from one lightweight agent.
01
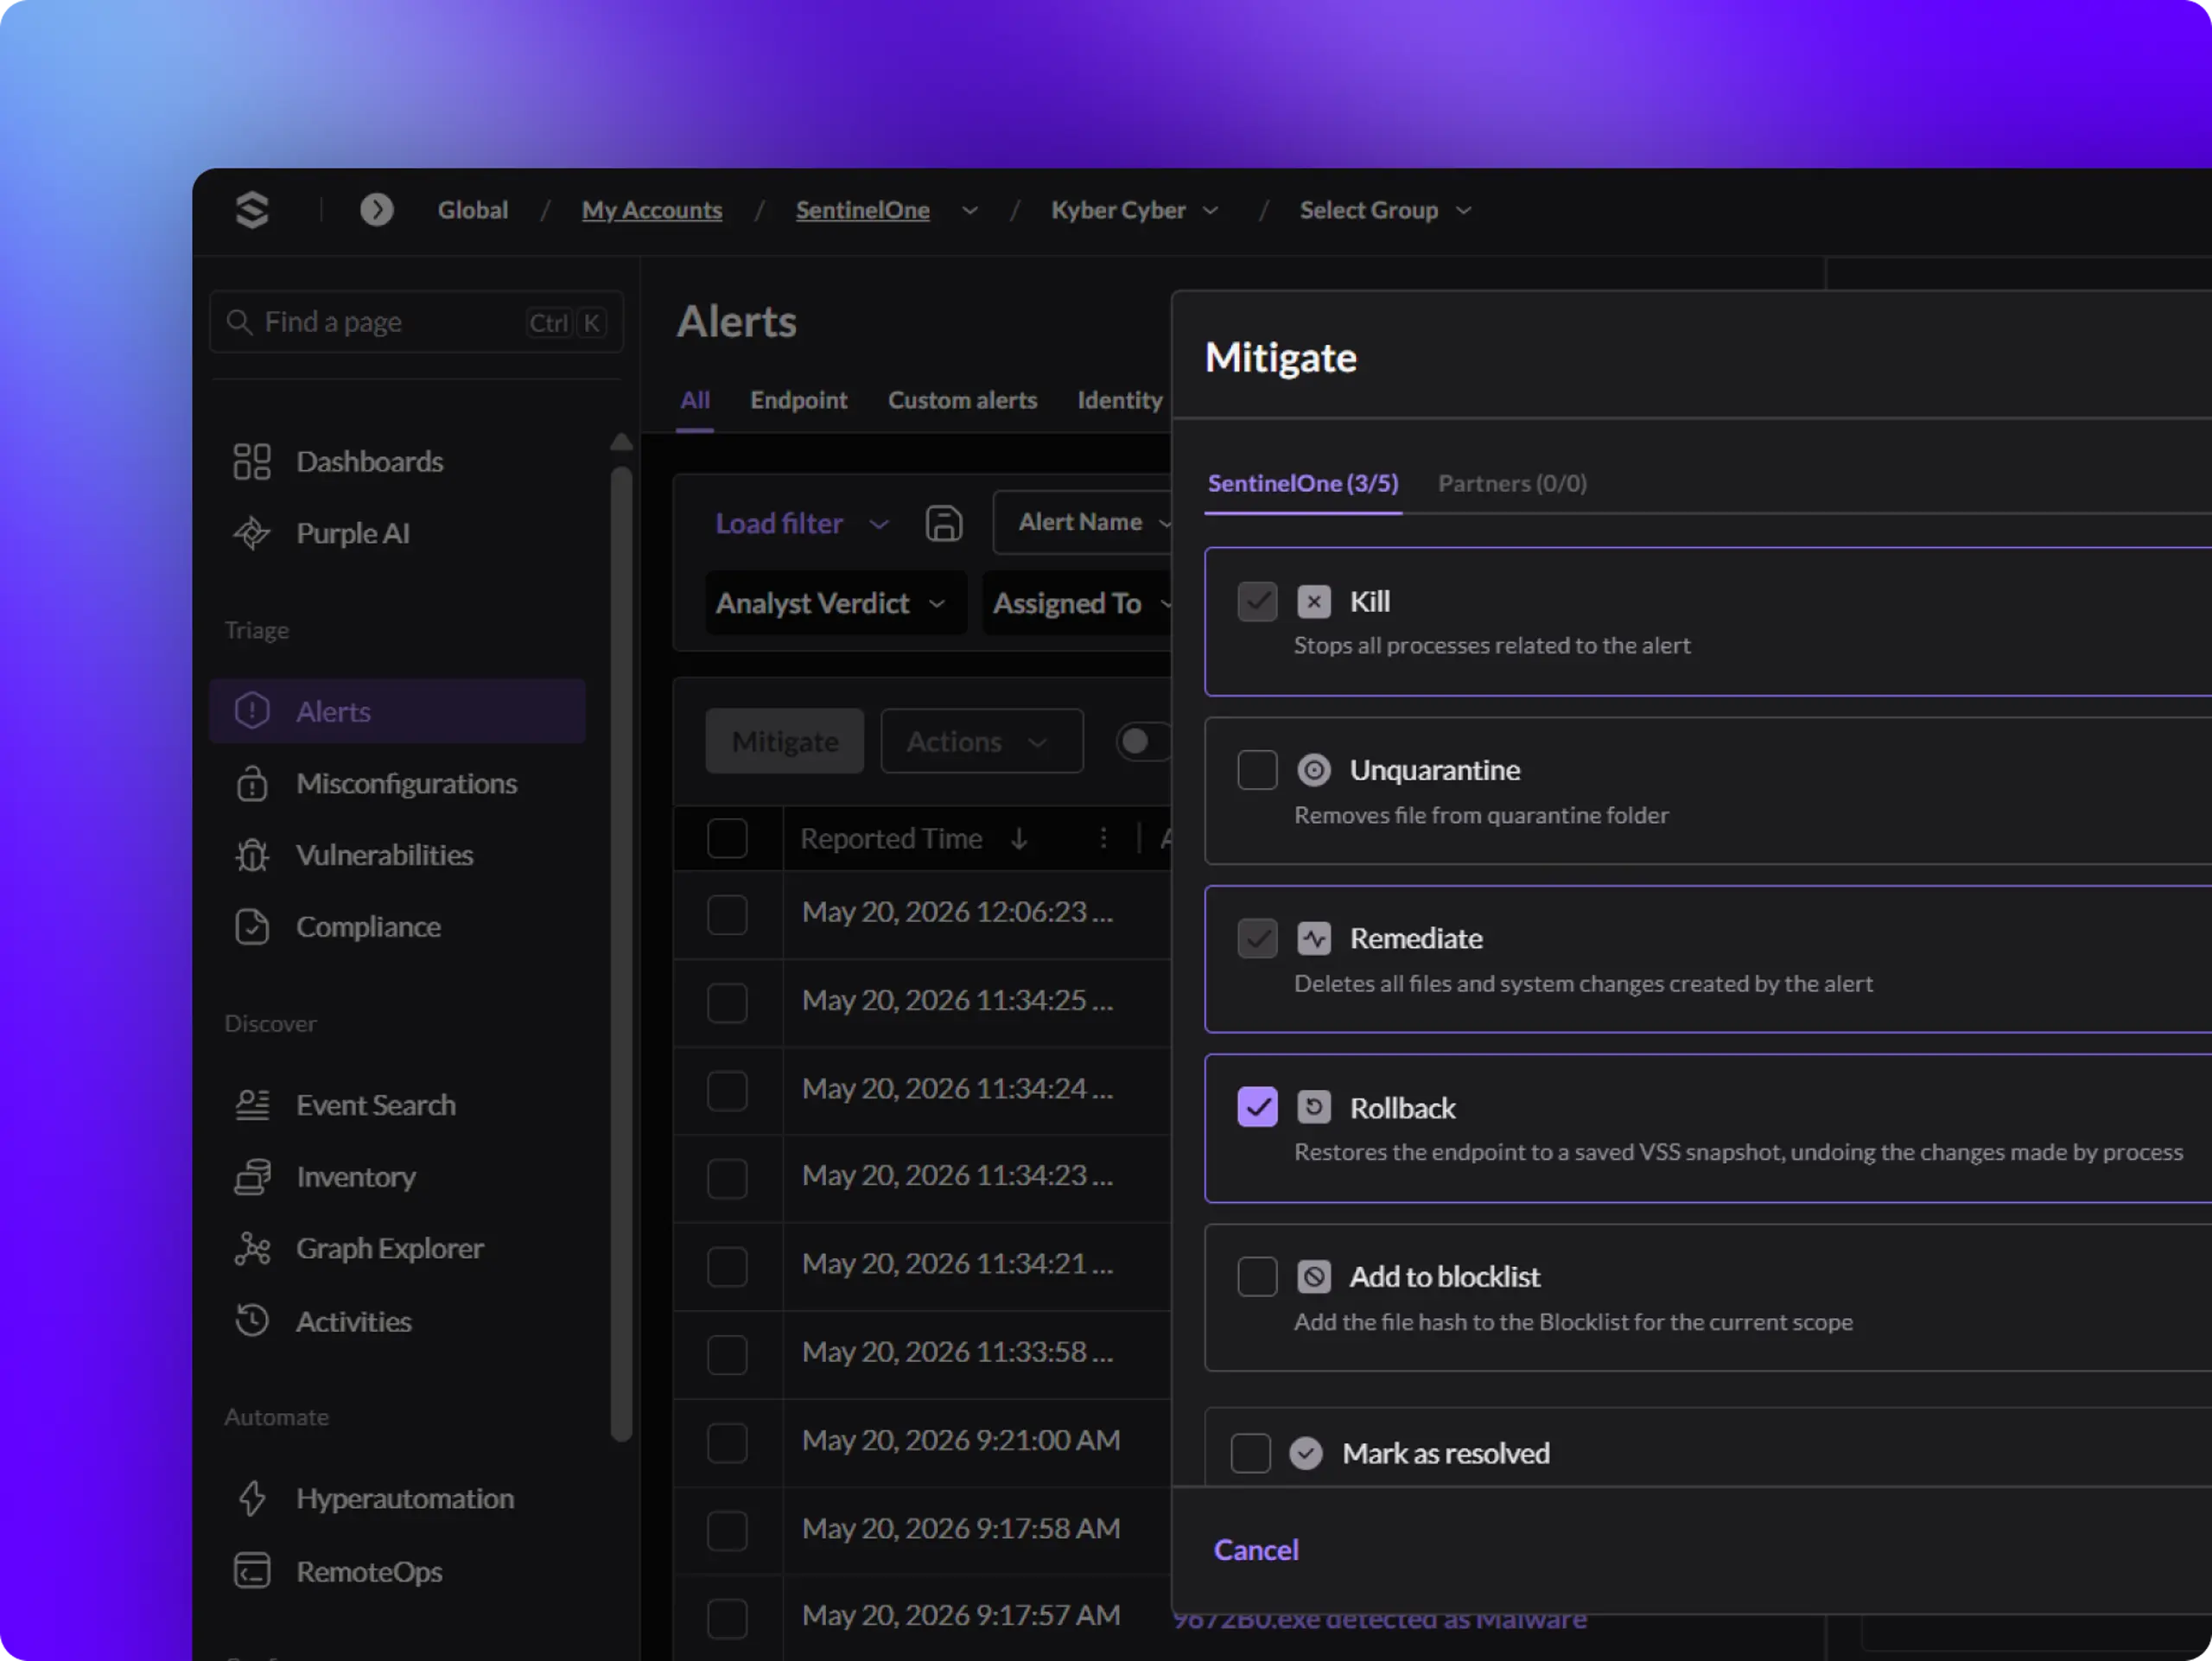
Dark security dashboard in a browser window with title Alerts and an open Mitigate modal showing ransomware actions: Kill, Unquarantine, Remediate, Rollback, blocklist, mark resolved; Cancel button

Endpoint Protection Platform (EPP)

See Threats Before They Execute

Shut the door on attackers at their first move.

  • Behavioral AI blocks malware, ransomware, fileless attacks, and zero days before execution. No signature updates needed.

  • If ransomware gets through, 1-click rollback restores encrypted files to their pre-attack state instantly. No manual recovery required.

  • Full protection online or offline, deployed across SaaS, on-premises, hybrid, and air-gapped environments.
02
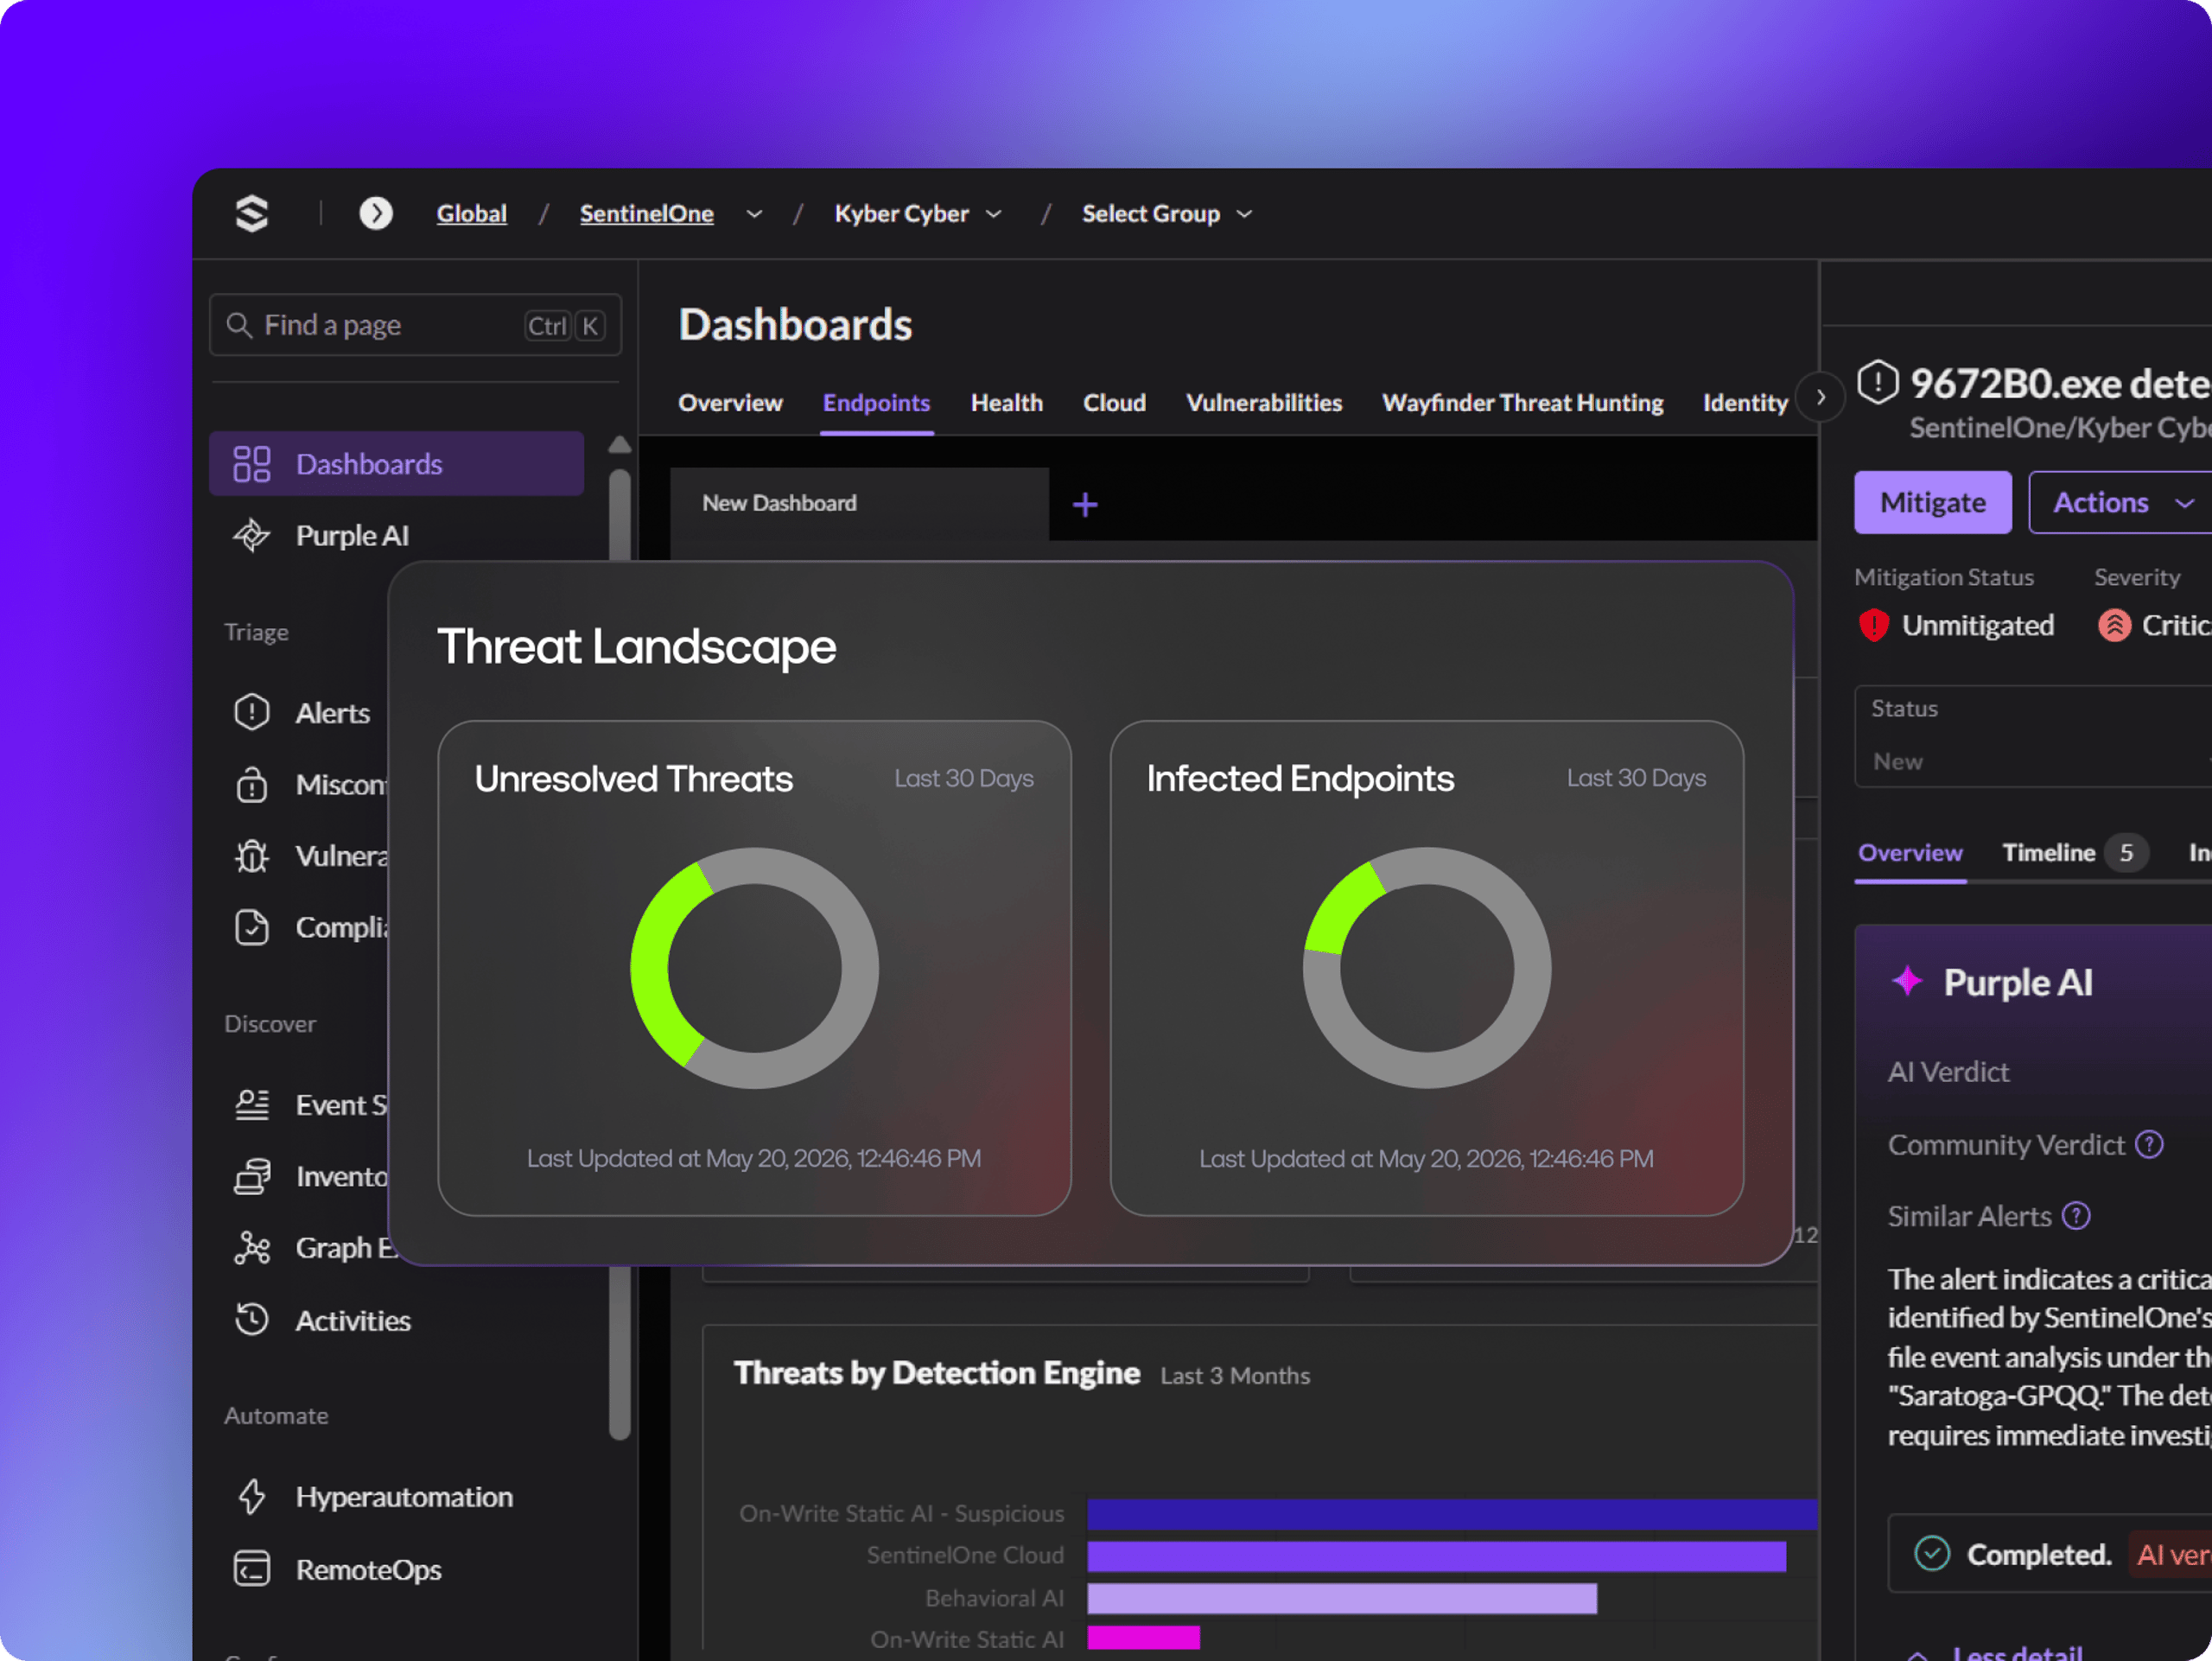
Dark cybersecurity dashboard UI with tabs like Dashboards, Threat Landscape card, donut charts (Unresolved Threats, Infected Endpoints), and Mitigate button

Endpoint Detection & Response (EDR)

Catch What Prevention Misses

See every threat that gets through. Respond in seconds.

  • Autonomous response kills malicious processes, isolates devices, and removes threats at machine speed, with no analyst intervention.

  • Ask Purple AI in natural language to investigate alerts, hunt for threats, and surface the full attack story in seconds.

  • Every attack is reconstructed into a complete forensic Storyline™, showing exactly what happened, when, and how it spread.

03
Man at desk looking at dark monitor; red glasses, striped shirt, blue lanyard; overlay UI lines and small unreadable text

EPP + EDR Combined

One Agent. Less Risk. Total Control.

Cut cost and complexity. Without cutting coverage.

  • A single lightweight agent handles prevention, detection, and response, replacing your antivirus, standalone EDR, and SIEM.

  • Protect 100 or 100,000 endpoints from a single console, across Windows, macOS, Linux, cloud workloads, and mobile.

  • Compliance-ready out of the box for SOC 2, ISO 27001, HIPAA, PCI-DSS, and FedRAMP.

Business Value

Coverage at a Fraction of the Cost

01

301%

Three-Year ROI

Singularity Endpoint pays for itself in as little as 11 months.

02

$126,900

Annual Benefits per 1,000 Endpoints Secured

$4.11M in avg. yearly value from efficiency gains, cost cuts, and reduced risk.

03

17%

Lower Security Solution Costs

Consolidate tools and cut licensing spend without losing coverage.

*IDC, The Business Value of SentinelOne Singularity Endpoint, 2026

WHY SENTINELONE?

Same Category. Different Class.

Legacy endpoint vendors still detect with signatures and respond with manual workflows. Singularity Endpoint was built to outpace both the threat and the legacy tools trying to stop it.
Abstract purple-blue glossy translucent 3D shapes on black, layered diagonally with grid outlines and a top bar and lower-right square panel

Behavioral AI. Not Signatures.

Static signatures miss what they haven't seen before. Our Behavioral AI model detects threats by what they do, not what they look like, stopping unknown attacks pre-execution.

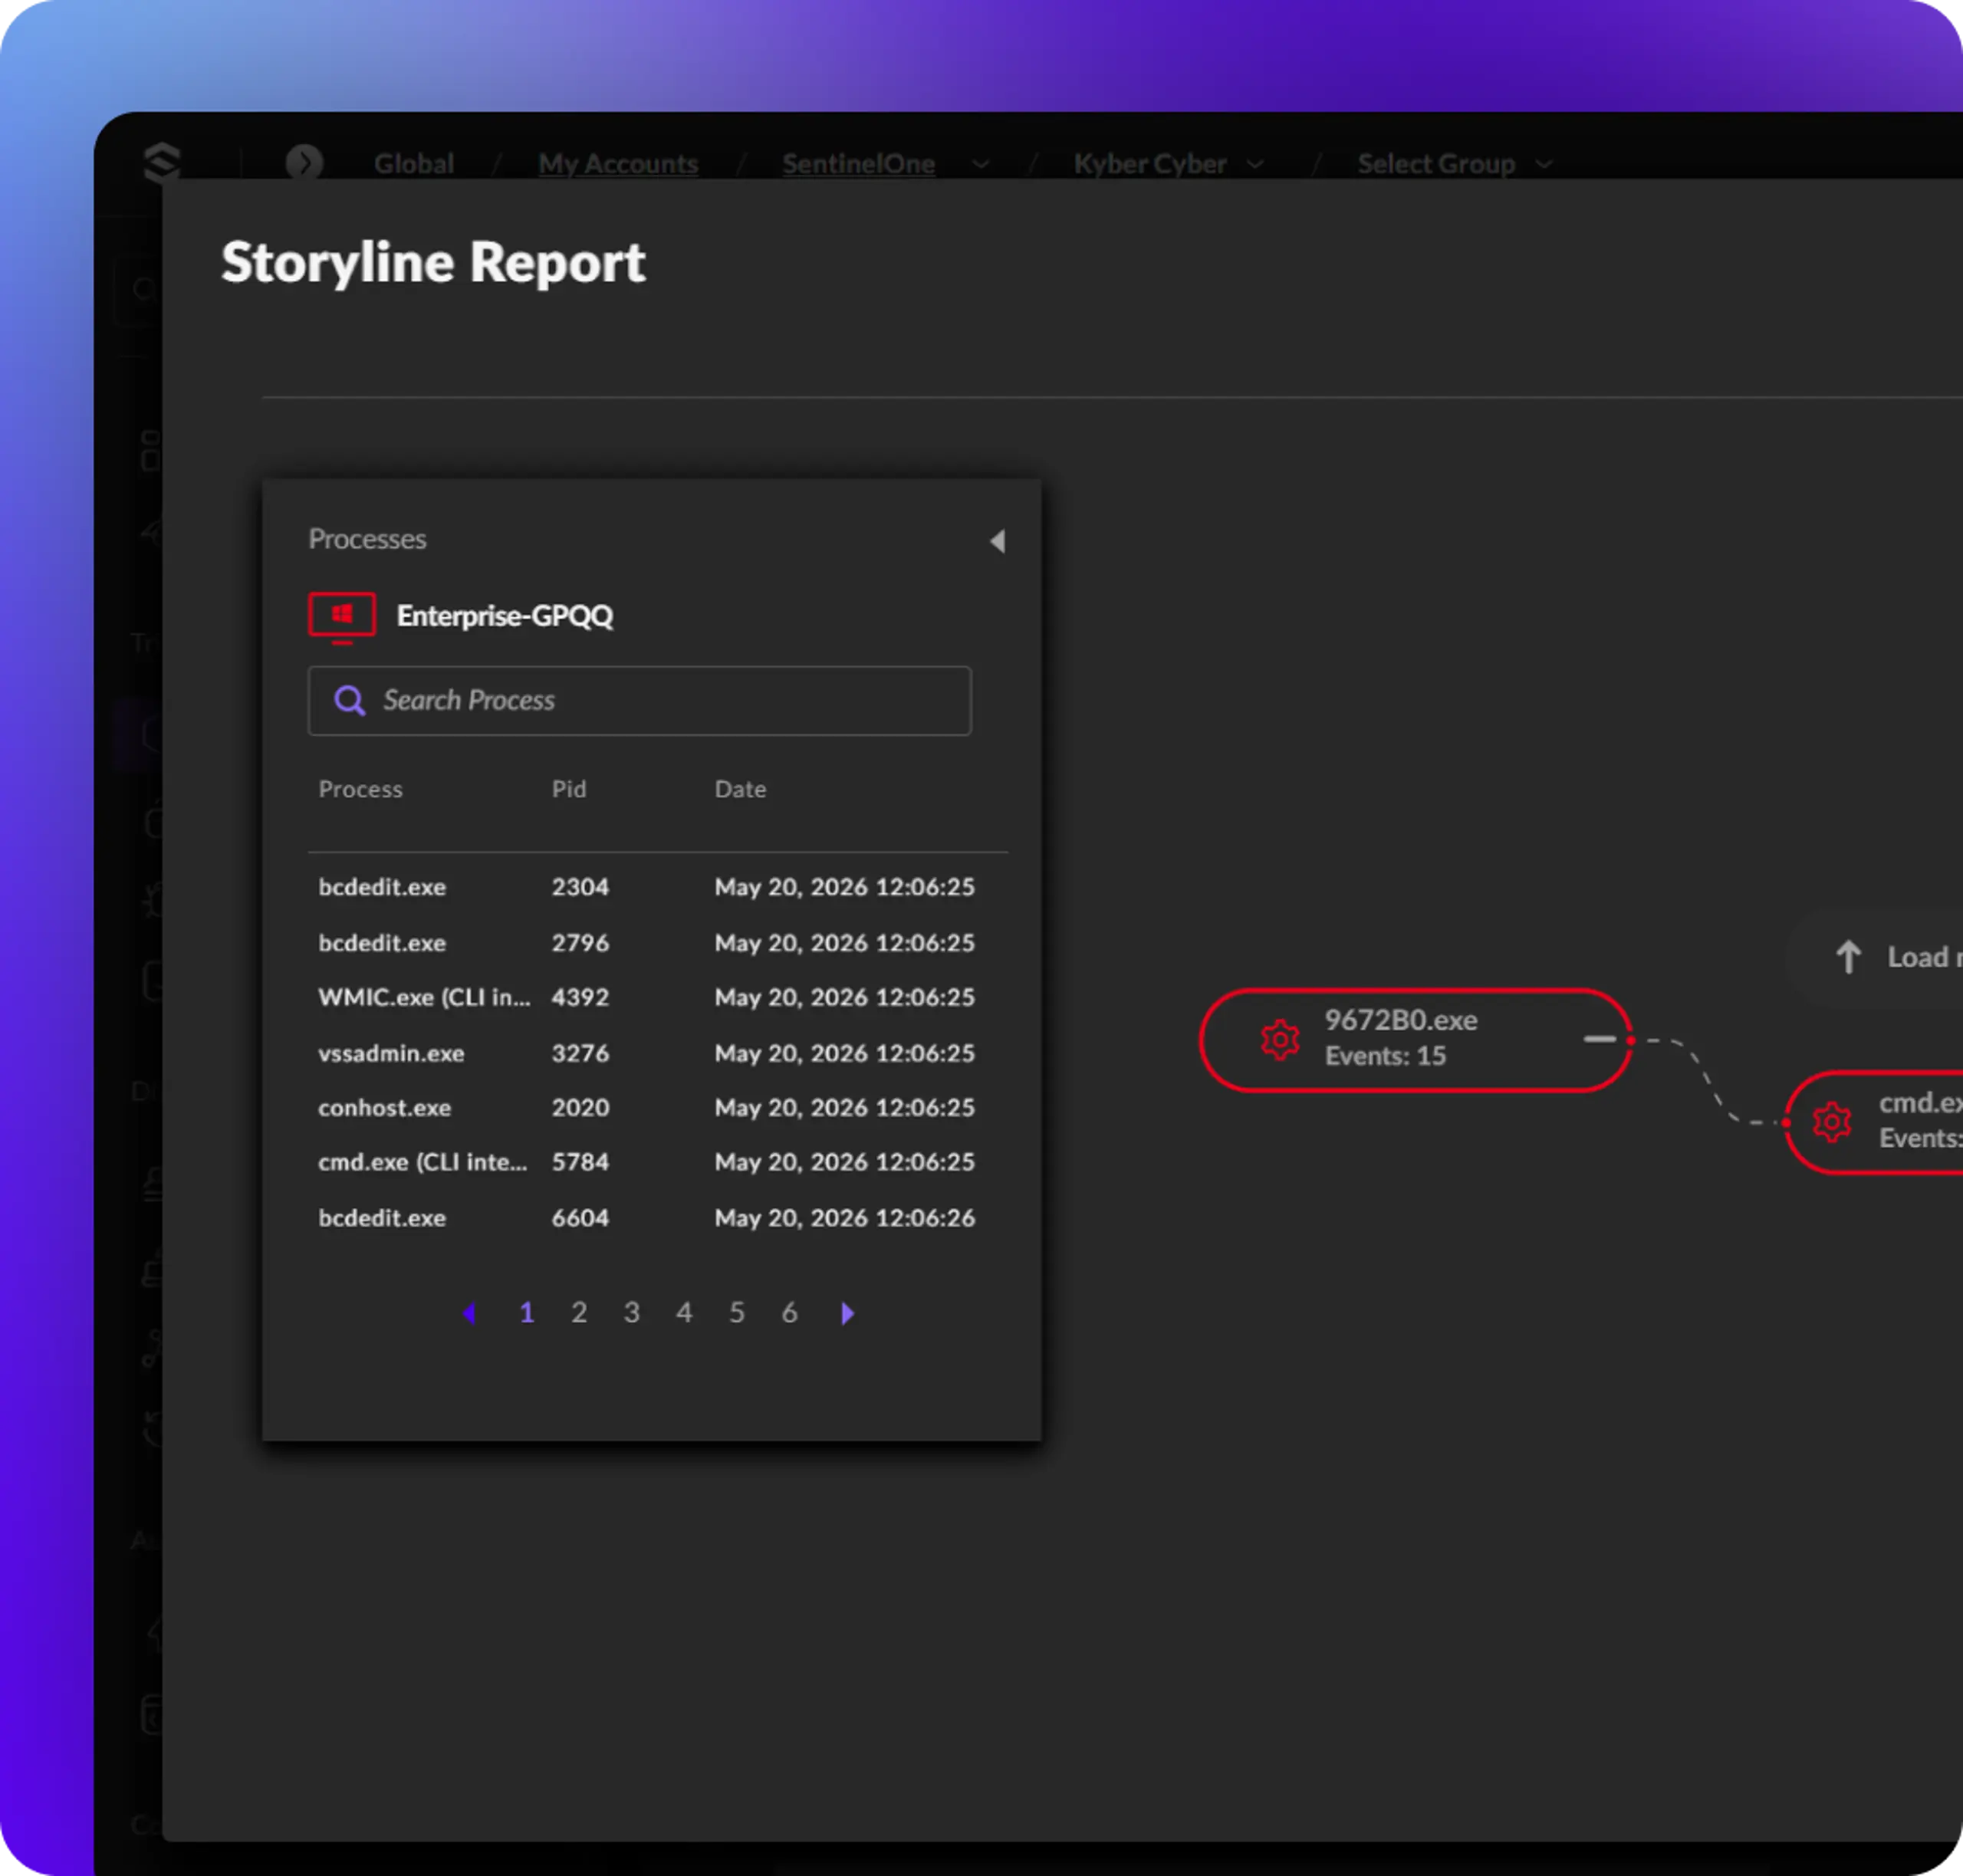
Dark “Storyline Report” dashboard with “Processes” panel listing .exe PIDs and dates, pagination 1–6, and red lineage boxes with Events 15

Storyline. Not Stitching.

Every related event is automatically correlated into a single attack narrative. Analysts see the full picture without manually connecting logs across tools.

Hands typing on a silver laptop keyboard beside an open notebook, with a checkered cup and faint interface-like overlay

One Agent. Not a Stack.

EPP, EDR, identity correlation, and response in a single lightweight agent. Fewer tools, fewer conflicts, less operational overhead across your entire fleet.

SUCCESS STORIES

Ask the Teams Who Run It Every Day

Arena scoreboard reading “CHASE CENTER” above a video screen of three people; crowd and pyrotechnic smoke jets rise

"SentinelOne 的單一平台可提供預防、偵測與回應功能,對我們而言是顛覆性的改變。擁有一套可即時監控威脅的集中式系統,為我們節省了寶貴的時間與資源。"

Brian Fulmer

Senior Director of IT at Golden State Warriors

閱讀案例故事
Close-up of a teal F1 race car cockpit and side body with “BOSS,” “aramco,” “SentinelOne,” “BOMBARDIER,” and “ASTON MA…” branding

“我們能夠在單一平台中擁有所有這些資料,並快速進行分析與決策,這對我們而言確實帶來了重大改變。”

Mark Carter

Chief Architect & Cybersecurity Officer at Aston Martin Aramco Formula One

閱讀案例故事
Low-angle construction site with rebar grid wall and a worker in a yellow-green hi-vis jacket bent over on gray ground

“與我們先前的供應商相比,SentinelOne 的表現有天壤之別。我們能夠輕鬆且快速地識別風險疑慮並進行修復。”

Dan Howard

VP of IT at Sundt Construction

閱讀案例故事

RESULTS

Proven by Analysts. Chosen by Practitioners.

The recognition that matters most comes from the evaluations buyers actually use to decide.
Dark navy rounded rectangle with white Gartner wordmark and small ® registered trademark symbol

領導者。連續六年

連續第六年獲評為 2026 Gartner® Magic Quadrant™ 端點保護平台領導者。

Navy rounded rectangle with white spaced serif text: “F R O S T &” over “S U L L I V A N”, with a cursive ampersand

頂尖表現供應商

在 Frost Radar™ Endpoint Security 2025 中獲評為頂尖表現供應商,並在成長與創新指數中皆名列領導者。

White stylized “FR” monogram on dark navy background above “FedRAMP” in red/pink text

FedRAMP High 已授權

已通過第三方評估並獲授權,可用於高敏感度的聯邦環境,進一步強化最高合規層級的信任。

NEED ANSWERS?

Frequently Asked Questions

An endpoint protection platform (EPP) is a security solution that prevents malware, ransomware, and other threats from executing on endpoints such as workstations, laptops, and servers. Modern EPP goes beyond static signatures by using behavioral AI to detect and block both known and unknown threats before they run, reducing reliance on signature updates and manual intervention.

Endpoint protection platforms (EPP) focus on preventing threats from executing. Endpoint detection and response (EDR) focuses on detecting threats that bypass prevention, investigating their scope, and enabling response actions like containment and rollback. Singularity Endpoint unifies both in a single agent and console, closing the gap between detection and containment that exists when EPP and EDR are separate tools.

Singularity Endpoint uses behavioral AI models that analyze what processes and users are doing in real time rather than matching against known threat signatures. This approach detects novel malware, fileless attacks, and living-off-the-land techniques that signature-based tools miss, stopping threats pre-execution based on behavior rather than prior knowledge.

Storyline is SentinelOne's automated correlation engine that connects every related process, file, network, and identity event into a single visual attack narrative. Instead of manually stitching logs across tools, analysts see the full attack path in one timeline. Combined with up to 365 days of EDR context retention, Storyline lets teams investigate incidents at any depth without losing historical context.

Explore Story

Singularity Endpoint deploys across SaaS, on-premises, hybrid, and air-gapped environments through a single lightweight agent. The platform is FedRAMP-High authorized for high-sensitivity federal deployments and provides Day 0 coverage for new macOS releases. Controlled update management gives IT teams full authority over when and how agent updates roll out across their fleet.

Singularity Endpoint integrates natively with Singularity Identity for endpoint-to-identity correlation, Purple AI for natural-language investigation and threat hunting, AI SIEM for cross-surface detection, and Wayfinder MDR for 24/7 managed coverage. Through the Singularity Marketplace, teams can also extend into XDR with one-click integrations across third-party tools.

Decorative background gradient

後續步驟

彌補落差。掌控端點。

取得個人化示範,了解 SentinelOne 與您目前的 EPP 或 EDR 解決方案相比表現如何。
Dark dashboard UI with purple-highlighted nav, summary cards showing 149, 7, 78, 56, 1.2 h, and a status table with linked purple text